Microsoft Teams will soon let administrators tweak the list of file extensions commonly associated with malware and security threats to meet their company’s security requirements.
This will come as an update to Weaponizable File Protection, a built-in Teams messaging safety feature that scans conversations and blocks chat or channel messages with dangerous, high-risk file attachments.
As detailed in a new Microsoft 365 roadmap entry, the feature is currently in development and will start rolling out in November 2026.
“Microsoft Teams is expanding admin controls for Weaponizable File Protection. Administrators will be able to customize which file types are blocked in Teams to align with their organization’s security requirements or continue using the Microsoft-recommended default list,” Microsoft says.
“This added flexibility helps organizations tailor file protection policies while maintaining a secure collaboration environment.”
When it reaches general availability, it will be available across Android, desktop, iOS, macOS, and web platforms for standard multi-tenant cloud environments worldwide.
Right now, according to Microsoft’s support website, admins can’t change the list of blocked file types.
Starting in December, admins can also block external users via the Defender portal to thwart cybercrime gangs(including ransomware groups) attempting to abuse Teams in social engineering attacks targeting victims’ employees.
Earlier this month, it said that Teams will get a new security feature designed to provide additional protection against phishing and fraud attempts by blurring QR codes sent by external senders.
This week, Microsoft also announced that, starting in November, it will let users report suspicious guest invitations directly from Teams to help their organization’s security teams identify and block phishing attempts and other attacks through guest invitations.
More recently, Microsoft has begun rolling out a new Teams meeting protection policy that lets admins automatically block all identified external bots from joining meetings.
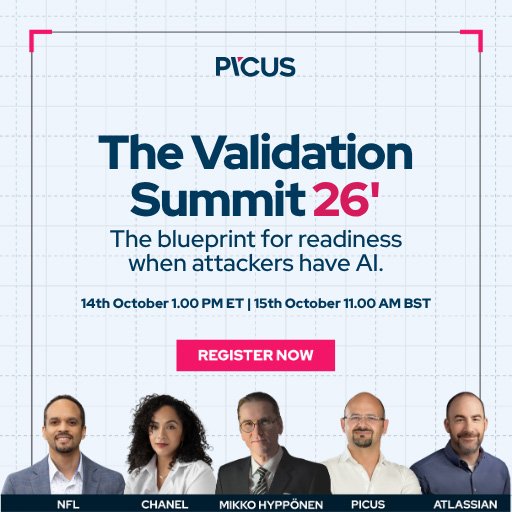
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Microsoft Teams to get efficiency mode on PCs with limited resources
Microsoft fixes Teams, Outlook launch failures on ARM Windows PCs
Microsoft says some users can’t open the Teams desktop client
Microsoft Teams, Outlook fail to launch on ARM-based Windows PCs
Microsoft Defender flags legitimate Google search links as malicious
Gyazo server flaw exploited to steal 23.6 million user records
Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
Watch a working exploit hit live controls and see exactly what blocks, detects, or misses
Patch automation needs more than speed. Action1 brings control into every stage of deployment.
Overdue a password health-check? Audit your Active Directory for free
Find out how long recovery really takes — and what it costs. Read the 2025 BCDR Report.
Automate Onboarding and Access Reviews with No-Code IGA: See how it works
Terms of Use – Privacy Policy – Ethics Statement – Affiliate Disclosure
Read our posting guidelinese to learn what content is prohibited.