Sweden’s data privacy regulator, IMY, has imposed a $183,000 (SEK 1.8 million) fine on IT systems provider Miljödata for inadequate security measures leading to a breach in August 2025 affecting 2.2 million people.
Miljödata is a Swedish software company that develops and provides work environment and HR management systems used by 80% of Sweden’s municipal systems.
Last year, on August 25, the company suffered a cyberattack that disrupted IT services in over 200 regions and compromised residents’ sensitive data.
The threat actor demanded a ransom of 1.5 Bitcoin (valued at $168,000 at the time) to prevent leaking the stolen information, but published it on the dark web under the name “Datacarry.”
The information included personal identity numbers, contact information, sickness absence, rehabilitation, and even school incidents involving underage individuals.
IMY launched an investigation in November 2025 to determine whether any security shortcomings violated the company’s obligations under the European Union’s General Data Protection Regulation (GDPR).
The agency has now confirmed that the company failed to adequately check newly installed software and lacked automated, real-time monitoring mechanisms to detect intrusions and suspicious activity.
“IMY’s investigation shows that the company did not maintain a sufficiently high level of technical and organizational security, considering the types of personal data it processed,” reads the announcement.
“The company did not perform sufficient checks when installing new software and did not have automated real-time monitoring of its systems to detect intrusions and suspicious activity.”
The negligence constitutes a violation of Article 32(1) of the GDPR, for which the agency imposed a penalty of $183,000.
Threat actors sometimes use the prospect of regulatory penalties to pressure victims into paying, and may set demands below what they believe an incident would ultimately cost, to incentivize victims to pay the ransom.
IMY noted that it has also launched investigations into two municipalities and one region in connection with the attack on Miljödata, which are ongoing, so additional penalties may be imposed in the future.
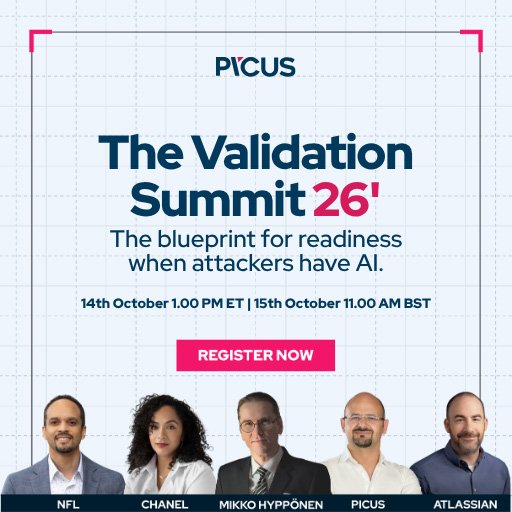
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
French hospital fined €500,000 after breach exposes data of 727,000
Google fined €403 million over location data privacy violations
Japan’s Digital Agency says VPN flaw exposed 246,000 personnel records
IDScan sued over alleged data breach affecting 153 million drivers
Berlin confirms data theft after Rhysida ransomware attack claims
Researchers escape OpenAI Codex sandbox to run commands on host
Malicious npm packages evade install-script defenses at runtime
Microsoft reminds admins to migrate Entra ID users to passkeys
Automate Onboarding and Access Reviews with No-Code IGA: See how it works
Overdue a password health-check? Audit your Active Directory for free
Build cyber resilience with Wazuh: The open-source SIEM & XDR for proactive protection
Overdue a password health-check? Audit your Active Directory for free
Find out how long recovery really takes — and what it costs. Read the 2025 BCDR Report.
Terms of Use – Privacy Policy – Ethics Statement – Affiliate Disclosure
Read our posting guidelinese to learn what content is prohibited.