Software

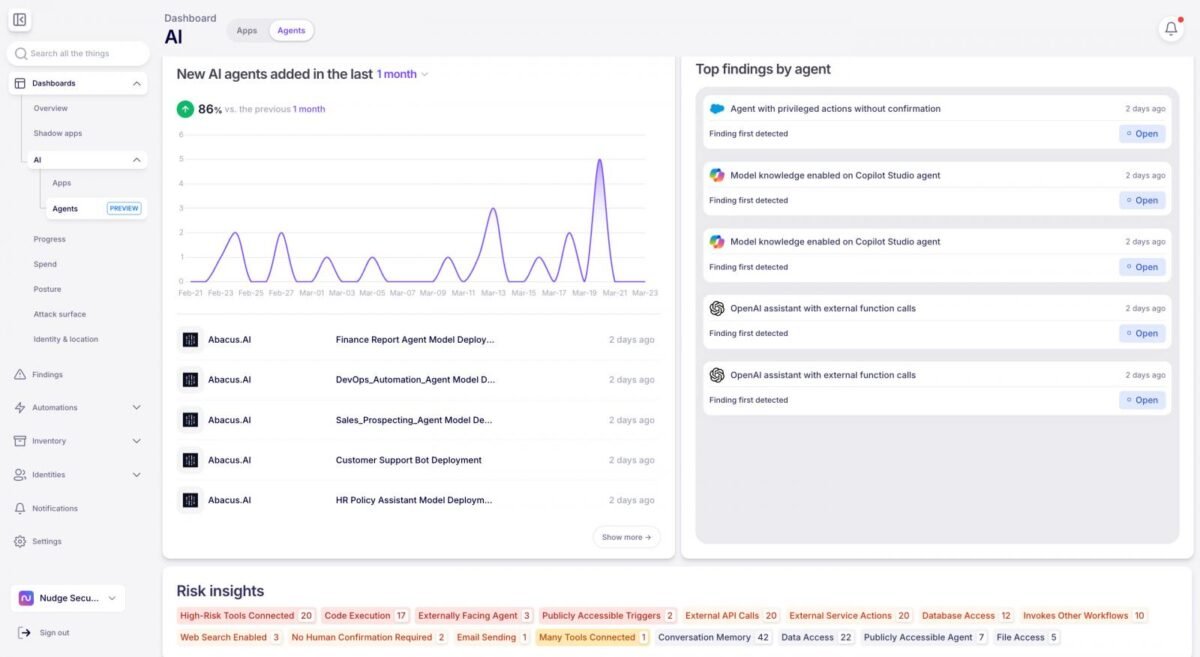
Shadow AI agents are multiplying. Here’s how to find and secure them.

Your workforce is building agents in Salesforce Agentforce, Microsoft Copilot Studio, Cursor, Zapier, Retool, and a dozen other tools, often without visibility or approval from IT or security. For IT and security teams, the decision of whether or not agents should be used has already been made by the business, one shadow agent at a

Shadow AI agents are multiplying. Here’s how to find and secure them. Read More »

Apple sued over fake App Store crypto wallet app stealing $1.8M in Bitcoin

Apple is being sued by three people who claim approximately $1.8 million in Bitcoin was stolen after downloading and using a fraudulent Sparrow Wallet application from the App Store. The complaint, filed on July 24 in California, alleges that Apple failed to adequately review and monitor applications distributed through the App Store while promoting the

Apple sued over fake App Store crypto wallet app stealing $1.8M in Bitcoin Read More »

New Certighost PoC exploit lets attackers hijack Windows domains

A proof-of-concept exploit for “Certighost,” a Windows Active Directory Certificate Services vulnerability, has been released that can allow authenticated attackers to potentially compromise a Windows domain. Tracked as CVE-2026-54121, the vulnerability was fixed by Microsoft as part of the July 2026 Patch Tuesday security updates. “An authenticated attacker could manipulate attributes associated with a machine

New Certighost PoC exploit lets attackers hijack Windows domains Read More »

New Dysphoria DDoS botnet spreads to 200k devices worldwide

A botnet called Dysphoria has compromised around 200,000 devices across the world and is using them for distributed denial of service (DDoS) attacks and traffic relay operations. According to QiAnXin XLab cybersecurity researchers, Dysphoria evolved from the ‘jackskid’ and ‘fbot’ malware by adding a covert blockchain-based command-and-control (C2) resolution mechanism. Specifically, the botnet uses Ethereum

New Dysphoria DDoS botnet spreads to 200k devices worldwide Read More »

Arista patches VeloCloud Orchestrator zero-day exploited in attacks

Arista has patched a maximum-severity command injection vulnerability in on-premises VeloCloud Orchestrator deployments that is being actively exploited in attacks. The vulnerability, tracked as CVE-2026-16812, is an unauthenticated OS command injection flaw with severity scores of 10.0, the maximum score that can be given to flaws. VeloCloud Orchestrator, also known as VCO, is a centralized

Arista patches VeloCloud Orchestrator zero-day exploited in attacks Read More »

Hackers target US firms in FastJson RCE zero-day attacks

Hackers are actively exploiting a vulnerability in the FastJson open-source Java library, allowing remote code execution without user interaction or elevated privileges. The security issue affects FastJson versions 1.2.68 through 1.2.83 and is leveraged in attacks targeting various organizations in the U.S. The malicious activity was observed last week by the agentic security company ThreatBook,

Hackers target US firms in FastJson RCE zero-day attacks Read More »

Jensen Huang’s first-ever post on X is in defense of open access to AI models, alongside Google, OpenAI, and Meta

Nvidia’s CEO Jensen Huang joined X last month, and recently made his first-ever post. As you could probably guess, it’s about AI. He argues, alongside companies like Google, OpenAI, and Meta, that the US should not aim to restrict open models ‘prematurely’, as they’re important for the growth of AI (among other things). Taking a

Jensen Huang’s first-ever post on X is in defense of open access to AI models, alongside Google, OpenAI, and Meta Read More »

Slopsquatting, Phantom Domains, and HalluSquatting Are the Same AI Attack

Three attacks, three names, and one identical flaw: AI coding agents treat a hallucinated identifier as a verified command. By Shane Warden, Principal Architect, ActiveState Ask an AI coding agent to fetch a tool. Occasionally, it returns a name that sounds right, but does not exist. Developers used to ignore this mistake, assuming a compiler

Slopsquatting, Phantom Domains, and HalluSquatting Are the Same AI Attack Read More »

Chick-fil-A data breach affects more than 13,000 customers

American fast food restaurant chain Chick-fil-A has confirmed that over 13,000 customers had their data stolen in a recent wave of credential stuffing attacks. As BleepingComputer first reported, the company revealed in data breach notification letters filed with multiple attorney general’s offices that it detected attacks targeting its website and mobile app between June 17

Chick-fil-A data breach affects more than 13,000 customers Read More »