Software

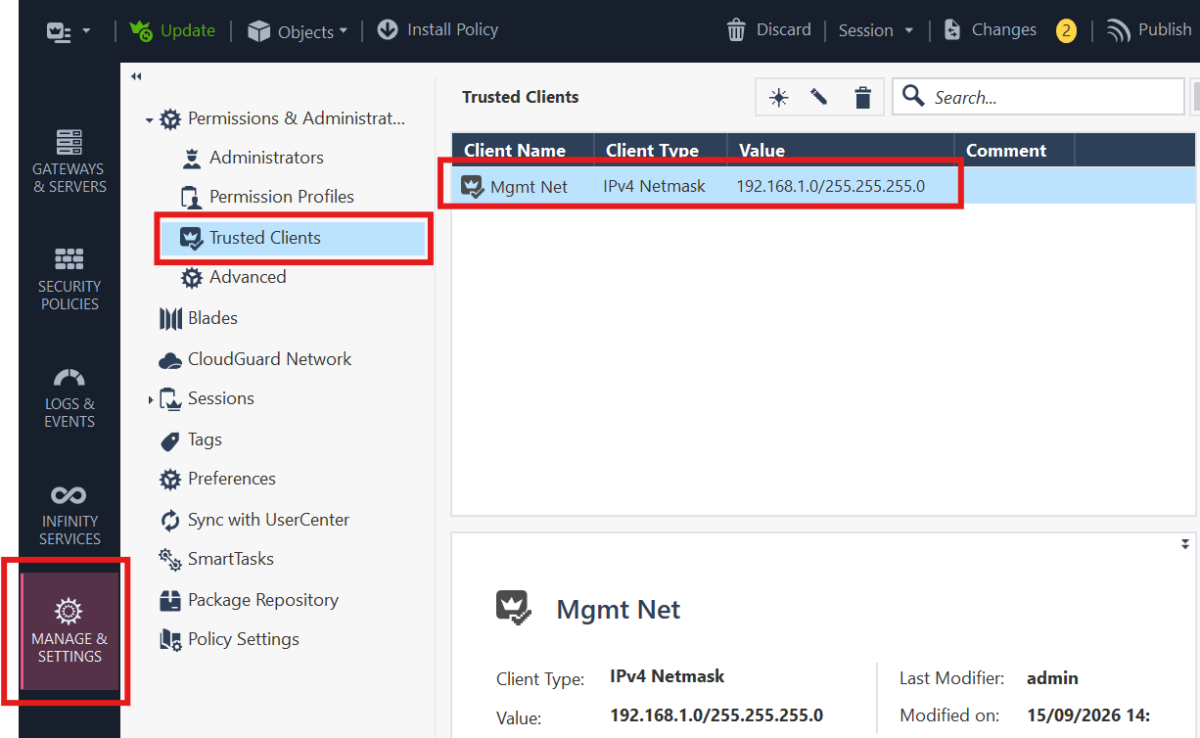
Check Point warns of Management Server zero-day exploited in attacks

Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts. The Security Management Server is a central repository that stores and manages security policies, processes administrator changes, and collects system logs across enterprise networks. Tracked as CVE-2026-93616, this path traversal flaw lets unauthenticated threat

Check Point warns of Management Server zero-day exploited in attacks Read More »
EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts

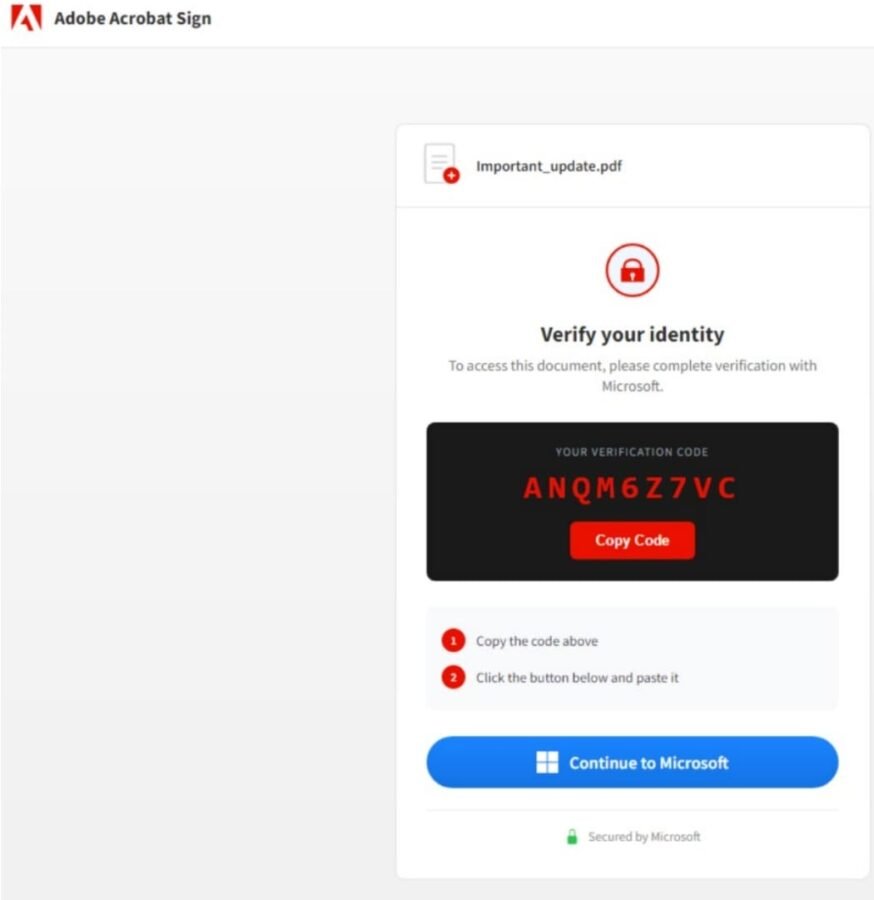
The EvilTokens platform that compromised more than 12,000 Microsoft accounts at over 10,000 organizations has been disrupted in an effort led by Microsoft’s Digital Crimes Unit (DCU). The phishing-as-a-service (PhaaS) operation emerged in February and was the first to support device code authentication at scale and offer cybercriminals AI-powered features for customizing lures and sifting

EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts Read More »

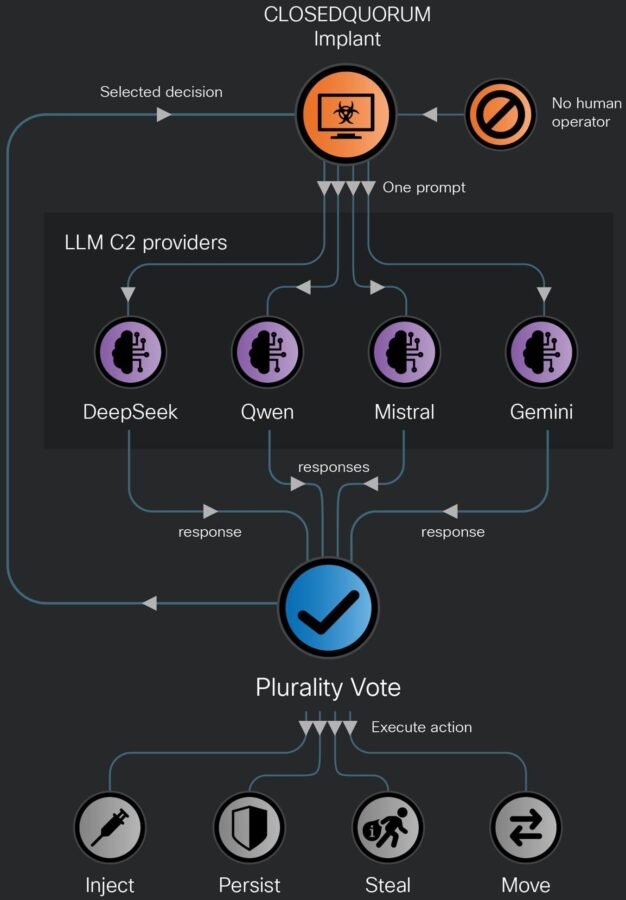
New ClosedQuorum Windows malware uses AI for attack decisions

A new Windows malware named ClosedQuorum uses Google Gemini, DeepSeek, Qwen, and Mistral AI models to autonomously determine the actions to take during post-compromise stages of an attack. The Go-based malware acts with no commands from a human operator, using reconnaissance information and a voting system to decide its next step on infected hosts. When

New ClosedQuorum Windows malware uses AI for attack decisions Read More »

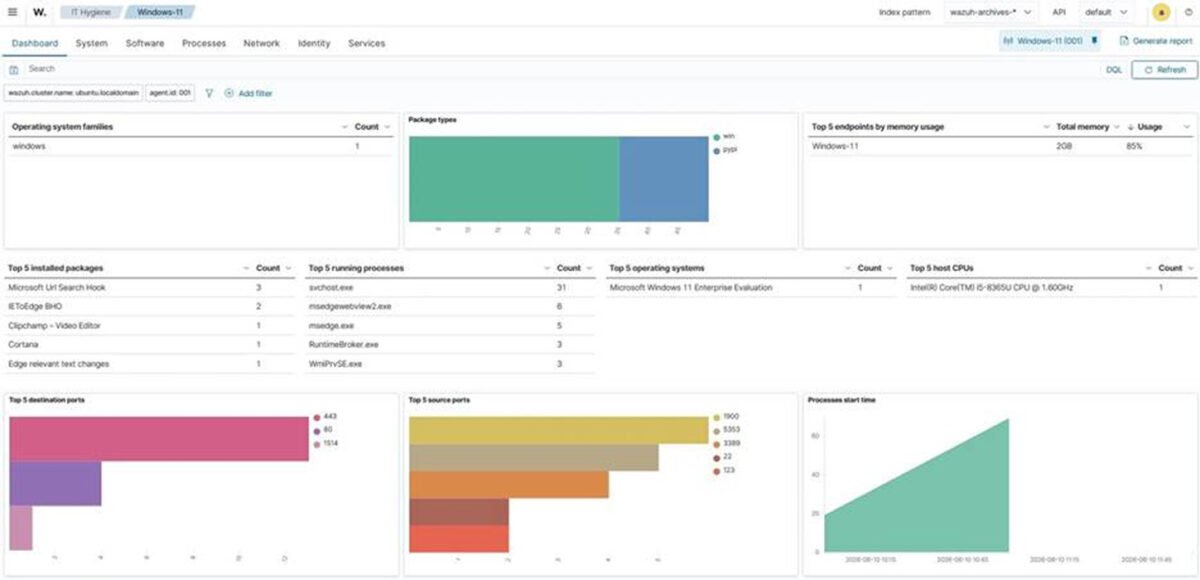
Reducing shadow IT visibility gaps with Wazuh

Shadow IT includes hardware, software, and services running outside IT and security teams’ visibility or approval. It can include unapproved applications employees install, browser extensions with excessive permissions, and endpoints provisioned once and never enrolled in any monitoring platform. These unmanaged assets create visibility gaps because existing security controls do not monitor them. Wazuh is

Reducing shadow IT visibility gaps with Wazuh Read More »

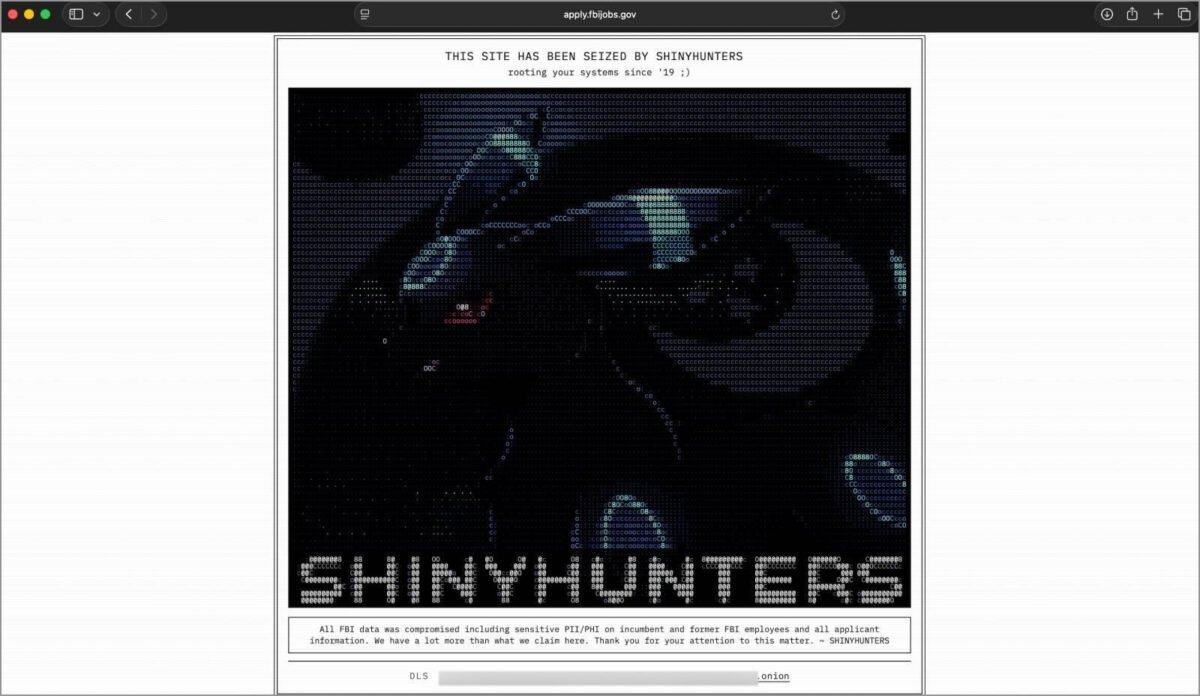
ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach

Update: Added the FBI’s statement below. The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, gaining access to internal services and stealing sensitive data on employees and job applicants. The threat actors told BleepingComputer the vulnerability allows remote code execution and that they used it Monday night to

ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach Read More »

Sweden fines Miljödata $183,000 over breach affecting 2.2 million

Sweden’s data privacy regulator, IMY, has imposed a $183,000 (SEK 1.8 million) fine on IT systems provider Miljödata for inadequate security measures leading to a breach in August 2025 affecting 2.2 million people. Miljödata is a Swedish software company that develops and provides work environment and HR management systems used by 80% of Sweden’s municipal

Sweden fines Miljödata $183,000 over breach affecting 2.2 million Read More »

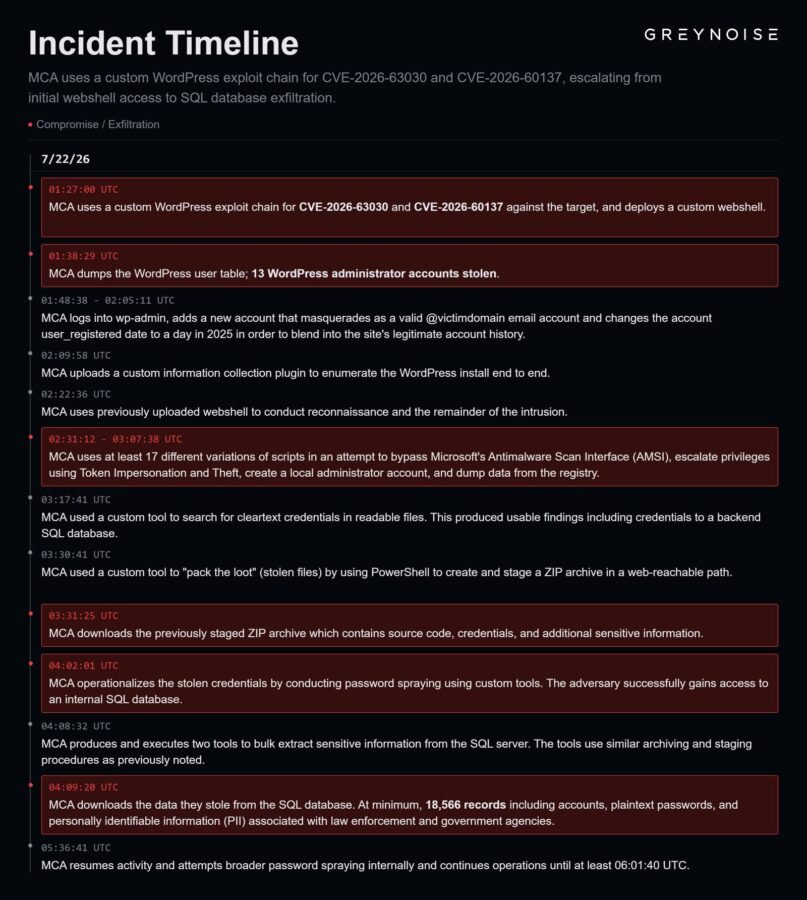
Chinese hackers exploit WordPress, Zyxel flaws to steal govt data

A Chinese-speaking threat actor has been exploiting vulnerabilities in ZyXEL GS1900 Smart Managed Switches and WordPress to steal sensitive data from 996 devices and more than 18,500 records stored in backend databases. The adversary targeted multiple technologies, including PAN-OS Global Protect, FlowiseAI, Nuclio, Proxmox, Ubiquity, with exploits for known security issues. Scans and attacks attributed

Chinese hackers exploit WordPress, Zyxel flaws to steal govt data Read More »

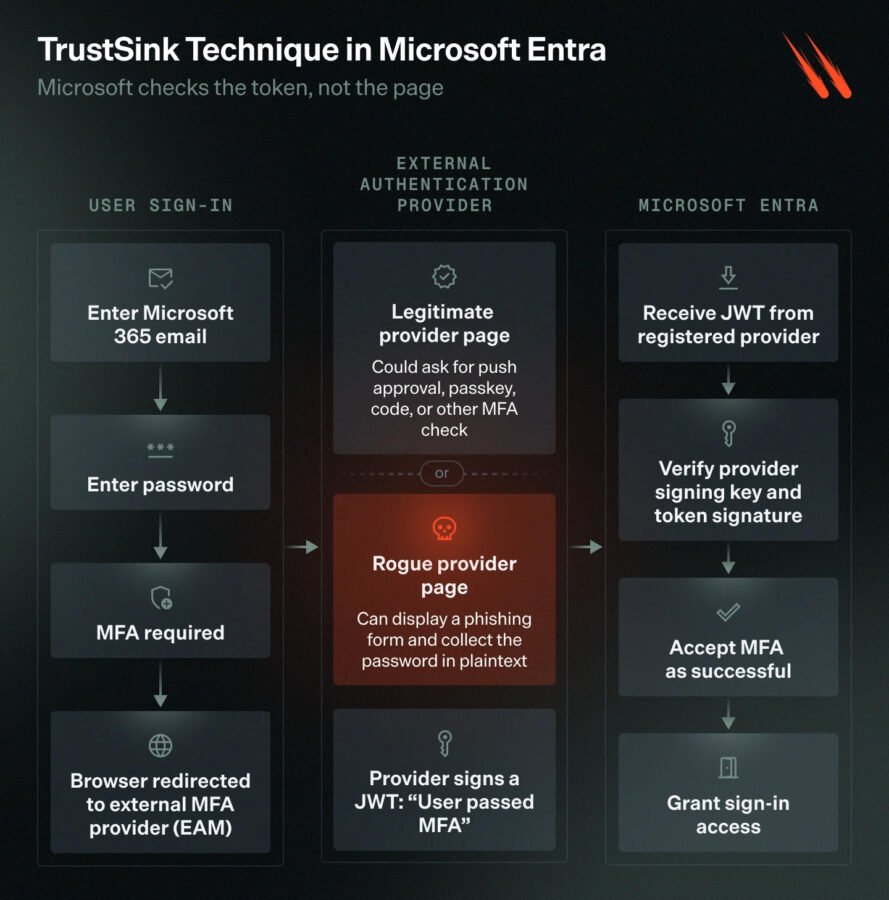
Rogue external MFA providers can steal passwords during logins

Security researchers developed an attack that lets hackers with privileged access register a rogue external MFA provider that steals users’ passwords during legitimate login attempts. The technique, dubbed TrustSink by Varonis Threat Labs, can work with any provider that relies on this external authentication model, though the researchers demonstrated the attack using Microsoft Entra. Microsoft

Rogue external MFA providers can steal passwords during logins Read More »

F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks

F5 has released security updates to address a critical BIG-IP APM zero-day vulnerability being exploited in remote code execution attacks. BIG-IP APM (short for Access Policy Manager) is the company’s centralized access management proxy solution that helps admins secure access to their organizations’ networks, applications, cloud, and application programming interfaces (APIs). Tracked as CVE-2026-94127, the

F5 patches BIG-IP APM zero-day flaw exploited in RCE attacks Read More »

Ryuk ransomware member sentenced to 24 months in prison

An Armenian man was sentenced to 24 months in prison and 3 years of supervised release for hacking U.S. companies and encrypting their systems in Ryuk ransomware attacks. 35-year-old Karen Serobovich Vardanyan (also known online as “Maneeken” or “Karl Lagerfeld”), who specialized in gaining initial access to corporate networks, pleaded guilty in July after being

Ryuk ransomware member sentenced to 24 months in prison Read More »