The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st.
Tracked as CVE-2026-104935, this high-severity authentication bypass vulnerability lets remote threat actors without privileges execute arbitrary commands on targeted ICS systems in low-complexity attacks that don’t require user interaction.
Ivanti released ICS versions 22.8R2.5, 25.1.3.0, 25.1.3.1, and 25.1.1.2 on Tuesday to address this security flaw and warned customers to “act immediately” because of “limited exploitation in the wild.”
While Ivanti didn’t share additional information about ongoing attacks targeting CVE-2026-104935, cybersecurity firm Volexity reported that an unknown threat actor it tracks as UTA0576 has been chaining this security issue with two other flaws in attacks since at least October 3rd.
“This exploit chain combined an authentication bypass, a remote code execution (RCE), and a privilege escalation vulnerability to achieve unauthenticated root-level code execution. The RCE and authentication bypass vulnerabilities are tracked under CVE-2026-104935,” Volexity said.
“Volexity identified a range of post-exploitation actions undertaken by the threat actor that targeted Active Directory credentials and secrets, including Local Administrator Password Solution (LAPS) passwords and BitLocker recovery keys.”
Threat intel firm Defused also confirmed Volexity’s report, saying it first found evidence that attackers are abusing CVE-2026-104935 in the wild on October 1st.
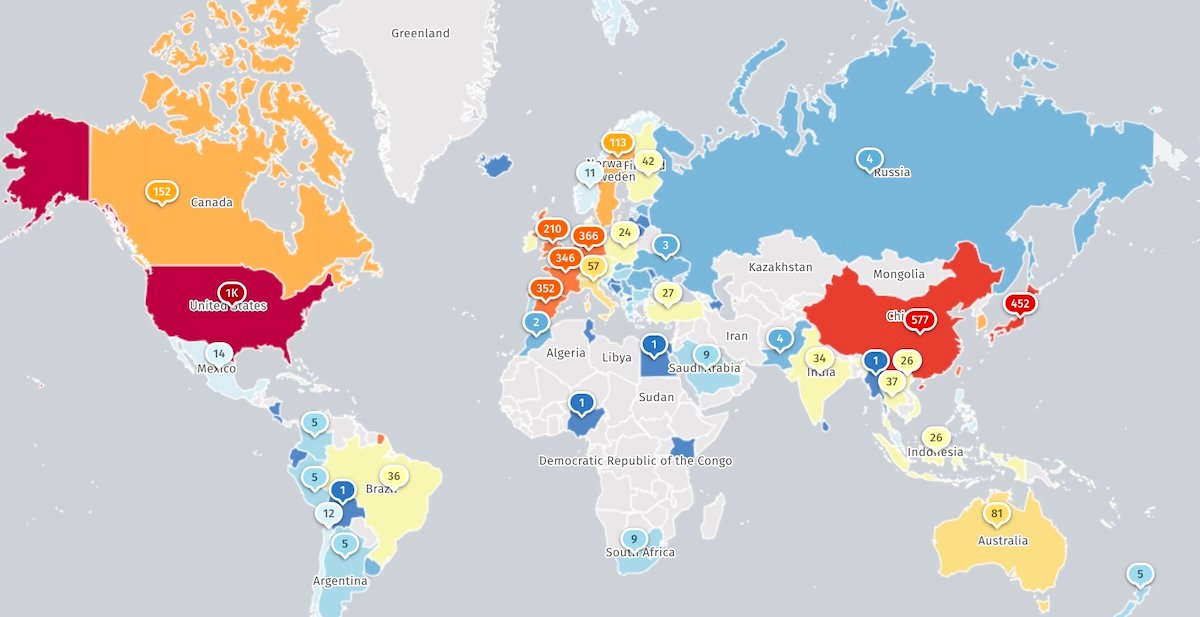
Internet threat watchdog Shadowserver now tracks over 5,600 Internet-exposed hosts with ICS fingerprints. However, there is no information on how many are secured against ongoing attacks or how many are honeypots designed to catch malicious activity.
On Tuesday, CISA also added CVE-2026-104935 to its list of actively exploited security flaws and ordered federal agencies to secure their networks against attacks by Friday, as mandated by its June Binding Operational Directive 26-04.
While BOD 26-04 applies only to Federal Civilian Executive Branch (FCEB) agencies, the cybersecurity agency also issued a separate advisory urging all security teams and network defenders to patch this vulnerability immediately and check for evidence of compromise.
“CISA is aware of cyber threat actors exploiting this zero-day authentication bypass vulnerability, which allows remote, unauthenticated execution of arbitrary commands, to conduct credential theft and data exfiltration. [..] CISA urges organizations with affected Ivanti Connect Secure appliances and deployments to immediately update to the latest version,” it warned.
“Organizations seeking to determine whether they were compromised will need to conduct network and memory forensics to identify evidence of exploitation. [..] Ivanti’s Integrity Checker Tool may not detect evidence of exploitation of CVE-2026-104935 because threat actor commands execute in memory.”
CISA advised defenders to take the following actions if they discover compromised Ivanti ICS appliances:
Ivanti addressed multiple other Connect Secure zero-days exploited in the wild over the last several years, including an authentication bypass (CVE-2023-46805) and a command injection (CVE-2024-21887) in early January 2024, and a server-side request forgery (CVE-2024-21893) two weeks later.
More recently, it patched a remote code execution (RCE) flaw (CVE-2025-0282) in January 2025 and another RCE vulnerability (CVE-2025-22457) that China-linked cyber spies have exploited since at least mid-March 2025.
CISA has added 36 Ivanti vulnerabilities to its list of actively exploited security issues since November 2021, 12 of which have also been abused in ransomware attacks.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Ivanti warns of Connect Secure zero-day exploited in attacks
Cisco warns of max severity ISE zero-day exploited in attacks
Citrix patches NetScaler SAML zero-day exploited in attacks
Fortinet warns of critical FortiMail flaw exploited in zero-day attacks
CISA orders feds to patch exploited Citrix flaws by Wednesday
Ledger confirms spy chip implant behind wallet crypto thefts
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days
Nippon Columbia malware incident exposes 8.6 million karaoke fan records
AI is a data-breach time bomb: Read the new report
Overdue a password health-check? Audit your Active Directory for free
Is your backup really out of reach? See what the latest attacks reveal.
AWS saw a valid key and let the agent clear a production bucket. See how Token Security ties each agent to its owner and limits it to read-only access.
New OAuth risk analyst agent: Turn 45 minutes of manual review into 15 seconds.
Move from visibility to action with AITEM, Criminal IP’s next evolution of ASM
Terms of Use – Privacy Policy – Ethics Statement – Affiliate Disclosure
Read our posting guidelinese to learn what content is prohibited.