A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide.
Since the start of the year, more than 750 million malicious messages have been aimed at Microsoft customers via email and SMS texts.
Following an investigation initiated by Microsoft and Japan’s National Police Agency (NPA) into a wave of fraudulent activity, “a sprawling Chinese-language cybercrime marketplace” was discovered, with tools and services for phishing campaigns.
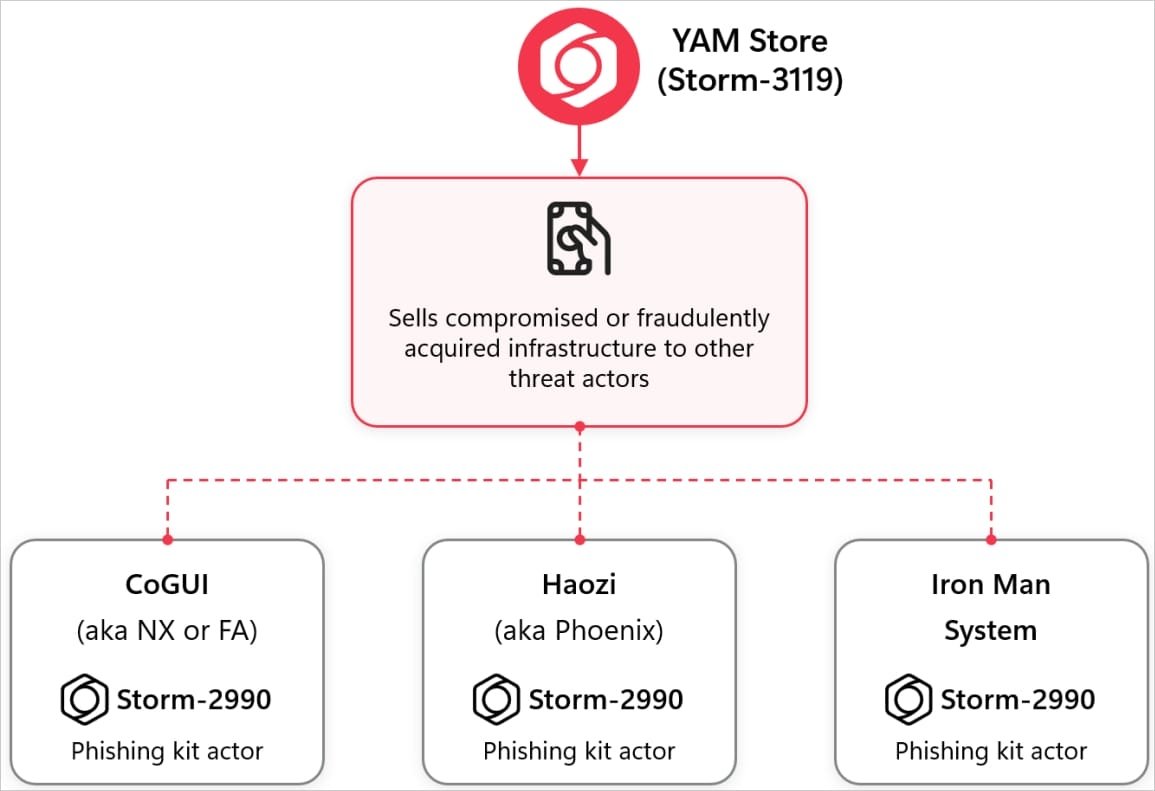
The investigators traced the malicious activity to YAM Store (Storm-3119), an underground infrastructure marketplace, then linked it to the CoGUI, Haozi, and Iron Man System phishing kits, collectively tracked as Storm-2990.
In a report today, Microsoft says that YAM Store sold compromised or fraudulently obtained Microsoft and Google environments, accounts, licenses, and storage.
Its operators acquired expired domains of real organizations, rebuilt websites to make defunct entities appear active, and then used those identities to obtain cloud accounts.
Another observed method was to generate fake organizations, complete with content and documentation, using AI tools.
In compromised Microsoft environments, the operators used stolen application credentials to manage accounts and licenses, and abused SharePoint and OneDrive storage for hosting.
The phishing kits offered cybercriminals a broad range of lures, including unpaid tolls, traffic penalties, delivery problems, and account verification requests.
The kits supported geofencing, fake CAPTCHA gates, IP filtering, and other measures to obstruct security analysis.
Microsoft says that CoGUI targeted victims in the United States and Japan, but Iron Man, which offers over 2,300 templates impersonating banks, retailers, delivery services, and government agencies, pushed it aside by mid-2026.
Cybersecurity company Resecurity also participated in the investigation and shared more details about Iron Man after analyzing exposed infrastructure, including a publicly exposed Git/container registry with 911 published builds and eight registered accounts.
The researchers also identified a product-selection subsystem linked to payment-card capture, cataloging 2,360 phishing packages covering 130 countries/areas, with updates through October 1, 2026.
Microsoft said the phishing platforms delivered over 750 million messages targeting Microsoft 365 customers, many using device-code phishing to obtain authentication tokens.
Under an order from the U.S. District Court for the Southern District of Florida, Microsoft and Health-ISAC seized and redirected domains supporting YAM Store, CoGUI, and Iron Man.
The tech giant also deactivated over 20,000 accounts associated with the YAM Store and blocked 100,000 domains the cybercriminals used for impersonation and fraud.
Currently, more infrastructure is being removed based on the findings of the investigation, which also involves the Japanese authorities, JC3, Resecurity, Cloudflare, Oracle, Proofpoint, and TRM Labs.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
Fake ChatGPT, Gemini Sites steal advertising accounts, MFA codes
BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations
AnonyMousKIT PhaaS uses voice AI agents to phish iPhone passcodes
Nikkei discloses breaches of employees’ Microsoft, Google email accounts
Former US Air Force members sent to prison over BEC attacks
Ledger confirms spy chip implant behind wallet crypto thefts
Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days
Nippon Columbia malware incident exposes 8.6 million karaoke fan records
Is your backup really out of reach? See what the latest attacks reveal.
Overdue a password health-check? Audit your Active Directory for free
New OAuth risk analyst agent: Turn 45 minutes of manual review into 15 seconds.
AI is a data-breach time bomb: Read the new report
Move from visibility to action with AITEM, Criminal IP’s next evolution of ASM
AWS saw a valid key and let the agent clear a production bucket. See how Token Security ties each agent to its owner and limits it to read-only access.
Terms of Use – Privacy Policy – Ethics Statement – Affiliate Disclosure
Read our posting guidelinese to learn what content is prohibited.