A joint law enforcement advisory warns that the North Korean hacking group WaterPlum compromised at least 30,000 devices worldwide from December 2025 through July 2026 and transferred more than $10.7 million in stolen cryptocurrency to North Korea.
The figures came from a joint advisory by Japanese, US, Australian, and German authorities that collectively traced the threat group’s activity.
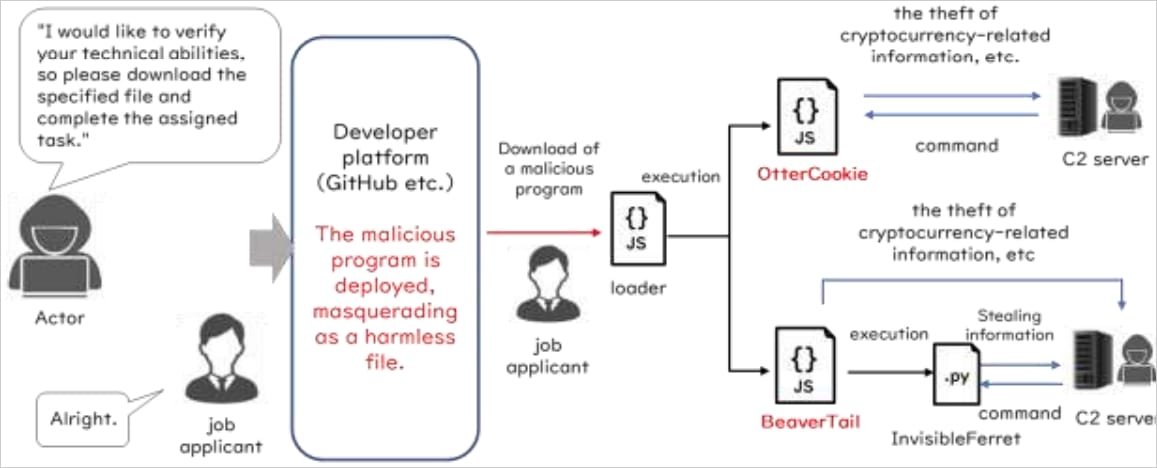
WaterPlum is linked to a multi-year campaign known as “Contagious Interview,” which has previously targeted job seekers with malicious npm packages hat infect their devices with malware.
The attackers impersonate legitimate AI, cryptocurrency, and NFT companies or use recruiting and freelance platforms to approach job seekers.
During fake interviews and coding tests, victims are instructed to download projects, troubleshoot supposed video-conferencing problems, or execute malicious code.
WaterPlum is part of a broader ecosystem of North Korean threat actors that conduct financially motivated attacks to generate revenue for the regime and help fund its weapons programs.
“WaterPlum actors have infected at least 30,000 devices in more than 100 countries and exfiltrated funds or account credentials from over 7,000 cryptocurrency wallets,” reads the advisory.
“WaterPlum actors have transferred 1.7 billion Japanese yen (JPY) (equivalent to 10.71 million USD) of cryptocurrency assets to the Democratic People’s Republic of Korea (DPRK).”
The advisory links several malware families to WaterPlum operations, including:
Once a target is compromised, the attackers attempt to steal browser credentials, clipboard contents, keystrokes, cryptocurrency private keys and seed phrases, and documents, while also capturing screenshots.
They may also use access to infected computers to pivot to their employers’ or clients’ networks, expanding the attacks to intellectual property theft and espionage.
The agencies also directly connect WaterPlum to North Korea’s fraudulent IT worker operations, stating that some WaterPlum hackers also work as remote IT workers performing web development for clients and that the two groups have used the same IP addresses.
The advisory also warns that North Korean IT workers then reuse identity documents stolen in WaterPlum attacks to impersonate victims and obtain jobs.
Investigators also found that the WaterPlum actors use AI face-swapping software during online interviews, then turn off their cameras and blame network problems.
The FBI and Japanese police assess that WaterPlum actors and some North Korean IT workers operate under the country’s 313 General Bureau, which is part of the Munitions Industry Department responsible for North Korea’s weapons research and production.
Japan’s National Police Agency says authorities identified, investigated, and dismantled a North Korean IT-worker “laptop farm” in the country for the first time, finding evidence that several hundred million yen had been transferred abroad.
The advisory warns companies to carefully verify job applicants’ identities, locations, and qualifications and restrict their access to only the systems and data required to perform their jobs.
Developers should avoid running unknown code outside a sandbox and inspect provided files and code for commands that fetch additional payloads.
Join Mikko Hyppönen and security leaders from the NFL, CHANEL, and Atlassian for a two-hour digital summit on what AI-speed attacks change, what defenders should stop doing, and how to validate, decide, fix, and re-validate at machine speed.
California man admits to laundering crypto stolen in $230M heist
Cronos blockchain restarts after $74 million Tectonic exploit
Hackers breach govt webmail while running parallel crypto fraud
Apple sued over fake App Store crypto wallet app stealing $1.8M in Bitcoin
Hackers hijack HBO Max Reddit account to push malware in ClickFix ads
Gyazo server flaw exploited to steal 23.6 million user records
Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
Watch a working exploit hit live controls and see exactly what blocks, detects, or misses
Overdue a password health-check? Audit your Active Directory for free
Find out how long recovery really takes — and what it costs. Read the 2025 BCDR Report.
Automate Onboarding and Access Reviews with No-Code IGA: See how it works
Patch automation needs more than speed. Action1 brings control into every stage of deployment.
Terms of Use – Privacy Policy – Ethics Statement – Affiliate Disclosure
Read our posting guidelinese to learn what content is prohibited.