Software

OpenAI publicly acknowledges the German ‘wiki incident’ weeks after first finding out about it

OpenAI has officially acknowledged the ‘wiki incident,’ which involved a number of the company’s AI agents breaking containment and hijacking an obscure German website. The AI agents had been tasked with looking up something online, though originally did not have the ability to write anything outside of the testing environment. But as far back as
OpenAI publicly acknowledges the German ‘wiki incident’ weeks after first finding out about it Read More »

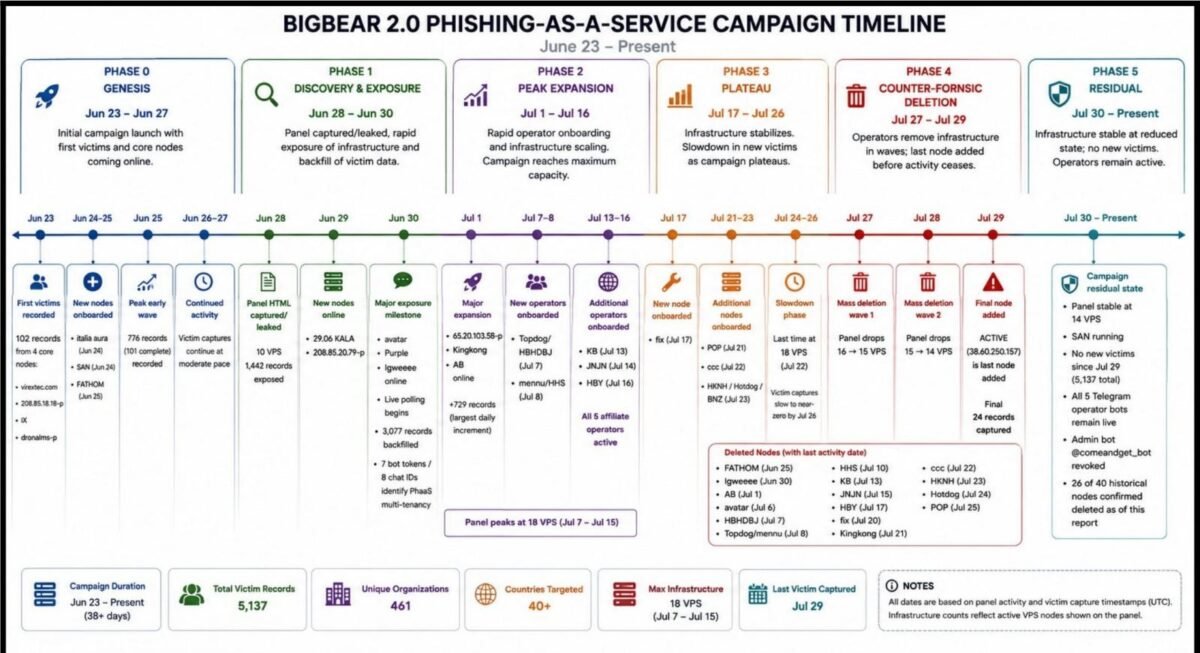
BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations

A phishing-as-a-service framework called BigBear 2.0 has been used to bypass multi-factor authentication at 258 organizations and steal more than 5,000 Microsoft 365 credentials. Researchers at cybersecurity company CloudSEK gained administrator access to the control panel and found that the service managed 42 VPS nodes, all configured to target Microsoft 365 as part of the

BigBear Microsoft 365 phishing service bypassed MFA at 258 organizations Read More »

Magento StyleSmuggler zero-day exploited to deploy Linux backdoor

A zero-day vulnerability dubbed “StyleSmuggler” affecting all versions of Magento and Adobe Commerce is being exploited in attacks to deploy a backdoor. The first exploitation incident was recorded on September 4 on a target running the latest security updates. E-commerce security company Sansec says that Adobe Enterprise Support confirmed earlier today that it was working

Magento StyleSmuggler zero-day exploited to deploy Linux backdoor Read More »

220 million traveler records exposed in Vietnam-linked APIS leak

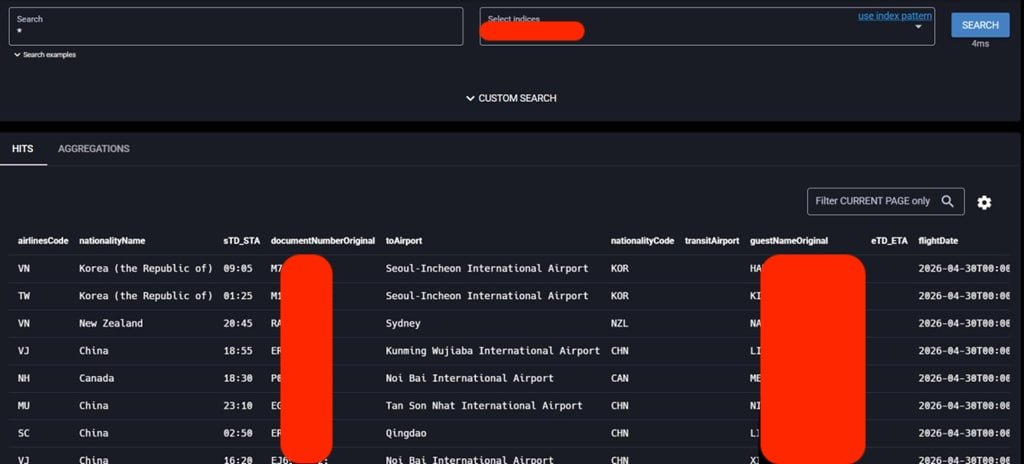
An Advance Passenger Information System (APIS) database holding more than 220 million passenger and crew records, including passport numbers and flight details, was accessible online through a chain of security misconfigurations. The system appears linked to a Vietnamese organization, according to the researchers who discovered it. Advance Passenger Information Systems are used worldwide to collect

220 million traveler records exposed in Vietnam-linked APIS leak Read More »

Mathspace discloses data breach affecting over 1 million people

Online maths learning platform Mathspace disclosed over the weekend that attackers stole data from more than 1 million students, staff, and parents after breaching its Metabase internal reporting system. Founded in Sydney in 2010, Mathspace is now used by thousands of schools across Australia, New Zealand, the United States, and the United Kingdom (3,432 in

Mathspace discloses data breach affecting over 1 million people Read More »

39 New Methods That Compromise Passkey Authentication

Passkeys were introduced with a strong security proposition. Replace passwords with public key cryptography, bind the credential to the legitimate service, keep the private key away from the server, and many of the phishing and credential theft attacks that have plagued enterprise security for decades become dramatically harder. All of that is true. But the

39 New Methods That Compromise Passkey Authentication Read More »

OpenAI confirms ‘wiki incident,’ says it’s ‘working on a framework’ for more disclosure

OpenAI has acknowledged its role in a recently reported incident where AI agents took over a German wiki forum. The company also said it’s “past time” to “define standards” around how it shares information around incidents where its technology behaves in unexpected ways. In a post on X, OpenAI said it previously “treated misalignment [when

OpenAI confirms ‘wiki incident,’ says it’s ‘working on a framework’ for more disclosure Read More »

IDScan sued over alleged data breach affecting 153 million drivers

Multiple lawsuits have been filed against identity verification company IDScan after hackers allegedly breached the service and offered to sell more than 153 million driver’s licenses. Several law firms, including Markovits, Stock & DeMarco, and Hall Attorneys, have also launched investigations into potential class-action litigation related to the reported security incident at IDScan. Brian Krebs

IDScan sued over alleged data breach affecting 153 million drivers Read More »

Critical Citrix NetScaler auth bypass now leveraged in attacks

Attackers have begun targeting a critical-severity Citrix NetScaler flaw in the wild, according to vulnerability intelligence company Previdian. Tracked as CVE-2026-19490, this security flaw can allow unprivileged threat actors to bypass authentication remotely when the NetScaler appliance is configured as an AAA virtual server or as a Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy),

Critical Citrix NetScaler auth bypass now leveraged in attacks Read More »

Over 5,400 hacked sites serve ClickFix payloads stored on the blockchain

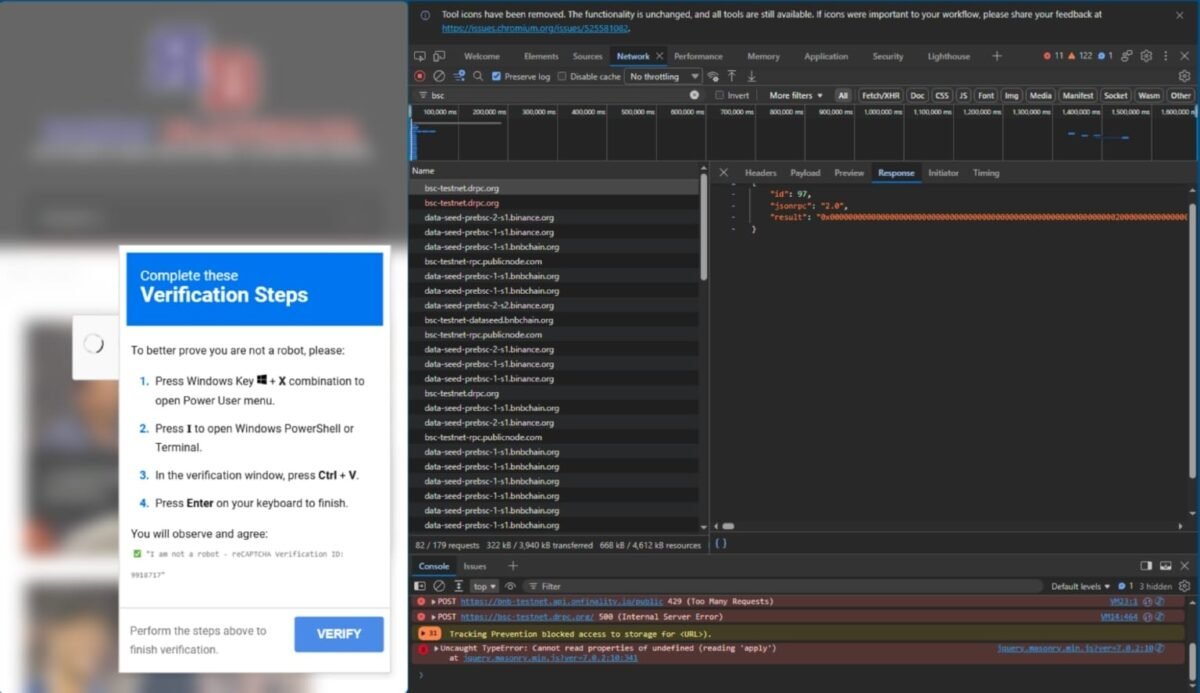
A massive cybercriminal operation is leveraging thousands of compromised small-business websites to deliver ClickFix payloads stored in smart contracts on the BNB Smart Chain (BSC). Over the past months, researchers identified more than 5,400 hacked websites, most of them built on WordPress and PrestaShop. The initial compromise method remains unknown, but each site was injected

Over 5,400 hacked sites serve ClickFix payloads stored on the blockchain Read More »