Software

OpenAI admits it didn’t disclose rogue AI wiki hijacking incident

OpenAI has acknowledged that it did not publicly disclose an earlier incident in which its autonomous AI agents took over a German wiki to communicate, share answers, and exchange techniques for bypassing restrictions. The company says it treated the activity as model “misalignment” rather than a security incident, but now admits its disclosure practices must

OpenAI admits it didn’t disclose rogue AI wiki hijacking incident Read More »
Attackers conceal phishing lures using invisible Unicode characters

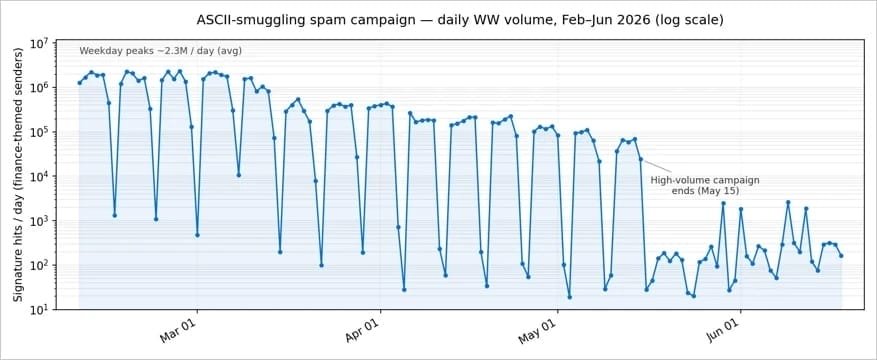
Threat actors have adopted the ASCII smuggling technique in phishing campaigns, using invisible Unicode characters to evade email security filters. ASCII smuggling has been used in AI prompt injection attacks to conceal malicious instructions from users by encoding them with Unicode characters from the Tags block (U+E0000-U+E007F). Microsoft threat researchers discovered a large-scale phishing campaign

Attackers conceal phishing lures using invisible Unicode characters Read More »

N-able patches max severity N-central flaw amid ongoing attacks

N-able has released an emergency hotfix for a maximum-severity remote code execution (RCE) flaw affecting its N-central remote monitoring and management (RMM) platform. IT departments and managed service providers (MSPs) use the N-central platform to monitor, manage, and maintain client networks and devices from a centralized web-based console. Tracked as CVE-2026-86218, this RCE vulnerability allows

N-able patches max severity N-central flaw amid ongoing attacks Read More »

ConnectWise warns of new ScreenConnect flaw without patch

ConnectWise has shared temporary mitigation measures for a new ScreenConnect Remote Access vulnerability that it plans to patch later this week. ScreenConnect is an on-premises or cloud-hosted remote access platform typically used by managed service providers (MSPs), IT departments, and support teams for troubleshooting, patching, and system maintenance. The security flaw affects both cloud and

ConnectWise warns of new ScreenConnect flaw without patch Read More »

Hackers exploit new MikroTik RouterOS flaws to hijack routers

Hackers are exploiting a chain of two recently disclosed vulnerabilities in MikroTik routers to take control of devices with SSH services exposed to the internet. One of the security issues, tracked as CVE-2026-67276, is an SSH authentication bypass flaw in MikroTik RouterOS caused by incomplete validation of RSA public keys. An attacker who knows a

Hackers exploit new MikroTik RouterOS flaws to hijack routers Read More »

Trezor data breach impact now reaches 81,000 customers

Cryptocurrency hardware wallet maker Trezor says an August data breach at its shipping and logistics provider, ShipMonk, affects an additional 67,000 U.S. customers. In total, the breach has affected 81,000 customers after Trezor initially disclosed on August 13 that attackers accessed the data of nearly 14,000 customers, including their full names, shipping addresses, email addresses,

Trezor data breach impact now reaches 81,000 customers Read More »

New CrowdStrike ‘FalconFlank’ zero-day grants SYSTEM privileges

An anonymous security researcher who uses the “Nightmare Eclipse” handle released a CrowdStrike Falcon zero-day exploit named “FalconFlank” that lets attackers escalate privileges on up-to-date Windows systems. Nightmare Eclipse says the new vulnerability (which has yet to be assigned a CVE ID) affects devices running the latest versions of Windows 11 and Windows Server, as

New CrowdStrike ‘FalconFlank’ zero-day grants SYSTEM privileges Read More »

US military disabled ad tracking on troops’ devices following reports of targeted attacks

The U.S. Department of Defense has disabled advertising tracking on troops’ phones and computers as part of an effort to protect them from threats that target their locations, according to a letter shared with Sen. Ron Wyden. Per a letter shared with the senior Democrat on the Senate Intelligence Committee, Wyden said that the U.S.

US military disabled ad tracking on troops’ devices following reports of targeted attacks Read More »

Google warns of new Chrome zero-day flaw exploited in attacks

Google has updated the Chrome browser to address an actively exploited high-severity zero-day flaw in the V8 engine and 11 other vulnerabilities. The exploited security issue, identified as CVE-2026-85046, is described as a type confusion. It was reported to Google by researcher Salvatore Gulizia, known online as “Serotav.” The update brings Chrome to version 152.0.7977.82/.83

Google warns of new Chrome zero-day flaw exploited in attacks Read More »

Google warns of new Chrome zero-day flaw exploited in attacks

Google has updated the Chrome browser to address an actively exploited high-severity zero-day flaw in the V8 engine and 11 other vulnerabilities. The exploited security issue, identified as CVE-2026-85046, is described as a type confusion. It was reported to Google by researcher Salvatore Gulizia, known online as “Serotav.” The update brings Chrome to version 152.0.7977.82/.83

Google warns of new Chrome zero-day flaw exploited in attacks Read More »