Software

Nvidia puts its money where its mouth is on open weight AI, moving to buy Hugging Face for $13 billion

Nvidia has just announced that it intends to acquire Hugging Face, the biggest open platform dedicated to developing machine-learning applications. Considering Nvidia has been all-in on AI for the past few years—to the point that I barely remember the last time the company even mentioned gaming in an earnings call—it’s hardly a surprising move. What
Nvidia puts its money where its mouth is on open weight AI, moving to buy Hugging Face for $13 billion Read More »

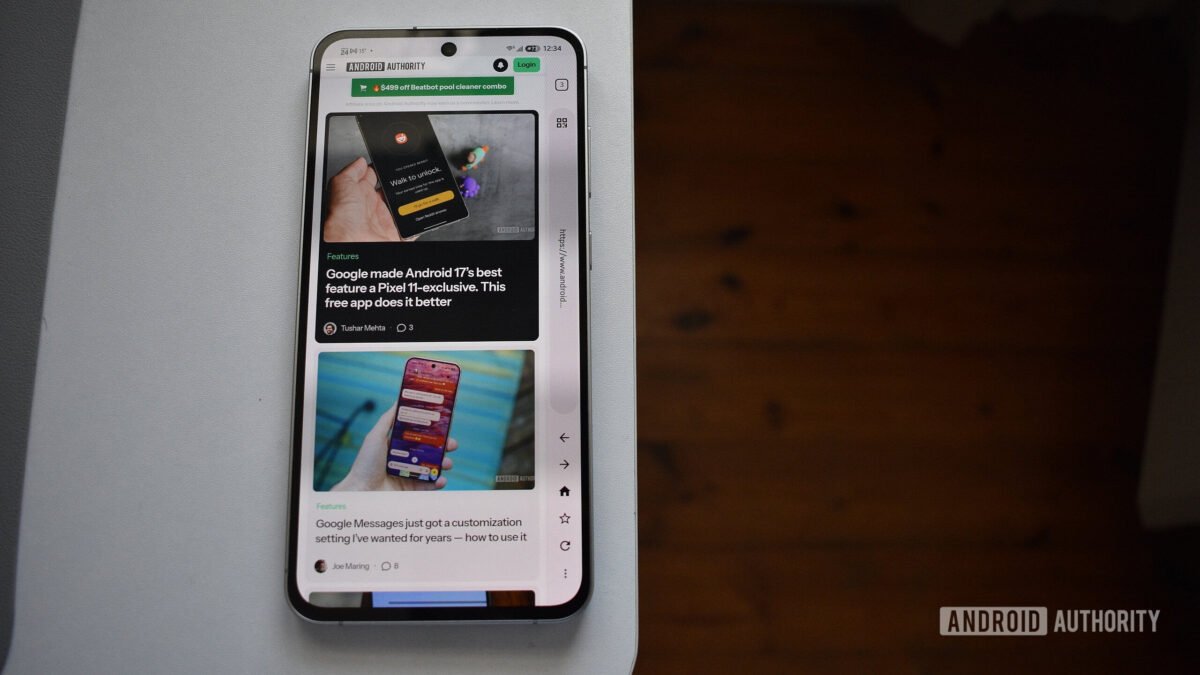
This Google Chrome alternative is the most exciting Android browser I’ve used all year

Affiliate links on Android Authority may earn us a commission. Learn more. Andy Walker / Android AuthorityAdd Android Authority on Google: Preferred SourceGoogle DiscoverIt’s usually difficult to get excited about a new Android browser. Unlike the launcher space, which includes a puzzle piece for almost every conceivable niche, browsers are mostly limited to two major

This Google Chrome alternative is the most exciting Android browser I’ve used all year Read More »

Plex warns users to patch security vulnerabilities immediately

Plex urged users this week to update their desktop clients and media servers immediately to patch multiple security vulnerabilities. These flaws have not yet been assigned CVE IDs for easy tracking, and while Plex didn’t provide additional details on Tuesday, the security issues are known to affect Plex Media Server v1.43.2 and earlier. Plex also

Plex warns users to patch security vulnerabilities immediately Read More »

Your Employee’s Password Appeared in an Infostealer Log. Now What?

Infostealer logs have evolved from an underground commodity into an operational security problem. For defenders, finding an exposed credential is only the beginning. In today’s reality many security analysts start their morning with an alert: an employee’s corporate email address has appeared in a newly collected infostealer log. The log contains a username and password

Your Employee’s Password Appeared in an Infostealer Log. Now What? Read More »

Critical Elementor Pro flaw exploited to take over WordPress sites

A recently patched critical vulnerability (CVE-2026-32475) in the Elementor Pro plugin for WordPress is being exploited in attacks that deliver a webshell payload and execute arbitrary commands on the server. Elementor Pro is a popular WordPress plugin with more than 6 million active installations, allowing users to build websites using a drag-and-drop interface. The CVE-2026-32475

Critical Elementor Pro flaw exploited to take over WordPress sites Read More »

HPE patches critical ArubaOS-CX remote code execution flaw

Hewlett Packard Enterprise (HPE) has patched a critical vulnerability in the ArubaOS-CX network operating system that could lead to remote code execution. Tracked as CVE-2026-73749, the security issue is a buffer overflow that allows unauthenticated remote attackers to send specially crafted packets to an affected daemon process, achieving code execution with elevated privileges. “Multiple vulnerabilities

HPE patches critical ArubaOS-CX remote code execution flaw Read More »

Coder’s registry infrastructure compromised to push malicious modules

Attackers compromised Coder’s Cloudflare infrastructure and added unauthorized registry servers that delivered malicious Terraform modules containing credential-stealing code. The Coder platform enables organizations to provide developers with secure, self-hosted cloud development environments for building and deploying software, including AI applications. The project is used by prominent private and government organizations, including Dropbox, Palantir, Square, Mercedes-Benz,

Coder’s registry infrastructure compromised to push malicious modules Read More »

French hospital fined €500,000 after breach exposes data of 727,000

France’s data protection authority (CNIL) has fined Hôpital privé de la Loire €500,000 ($580,000) for failing to adequately protect patients’ and their relatives’ data. The French agency says that the security failures led to a data breach in the summer of 2025, exposing sensitive data belonging to 524,867 patients and another 202,246 people designated as

French hospital fined €500,000 after breach exposes data of 727,000 Read More »

Norway considers ban on camera-enabled wearable ‘pervert glasses’

Norway is considering a ban on smart glasses and other camera-enabled wearable headsets as it seeks to regulate the controversial technology amid privacy concerns. The country’s digital minister Karianne Tung, as quoted by the AFP news agency, said that the government is looking to regulate the use of camera-enabled wearables, such as those made by

Norway considers ban on camera-enabled wearable ‘pervert glasses’ Read More »

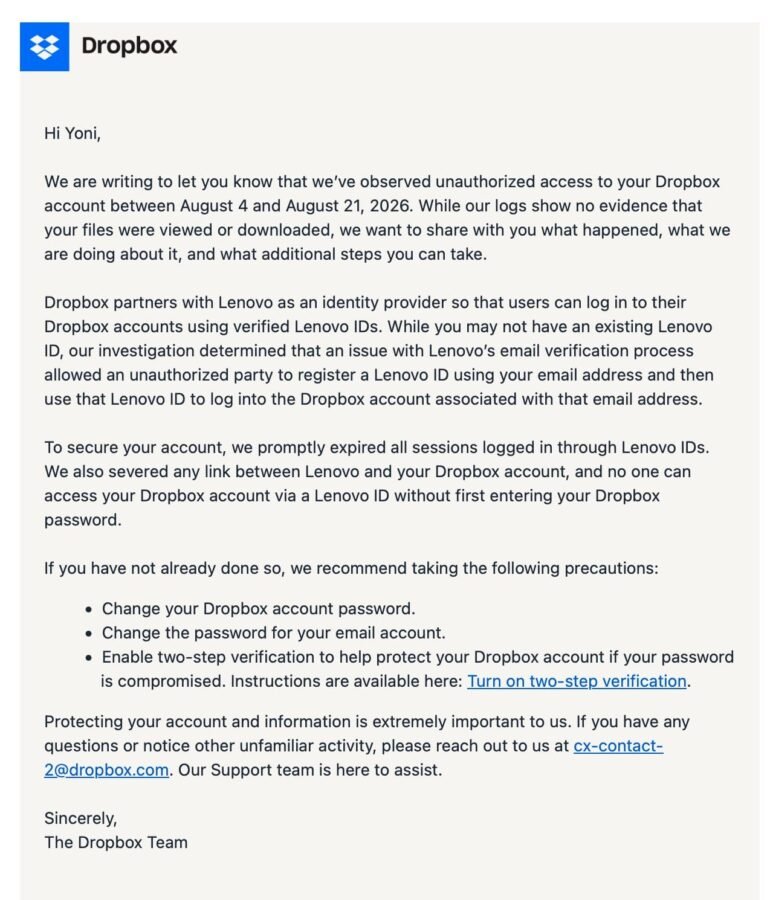
Dropbox accounts breached through Lenovo email verification flaw

Dropbox is warning some users that an unauthorized party accessed their accounts by exploiting a flaw in Lenovo’s email verification process to register fraudulent Lenovo IDs. Although some affected users did not have Lenovo accounts, the cloud-storage provider said it uses Lenovo Identity Provider Services as part of its authentication infrastructure. This allows users to

Dropbox accounts breached through Lenovo email verification flaw Read More »