Software

Critical Avada WordPress theme flaw enables zero-click RCE

A critical vulnerability chain in the popular Avada theme for WordPress can be exploited by an unauthenticated attacker to execute arbitrary PHP code on the server. The exploit chains six security issues into a zero-click attack. The flaws are collectively tracked as CVE-2026-18431 and received a 9.8 critical severity score. The attack comprises exploits for

Critical Avada WordPress theme flaw enables zero-click RCE Read More »

ATF confirms “major incident” after recent Qilin breach claims

ATF, the regulatory agency that enforces federal laws governing firearms and explosives in the United States, has confirmed that one of its systems was compromised after breach claims made by the Qilin ransomware gang. This follows Qilin adding the U.S. Bureau of Alcohol, Tobacco, Firearms and Explosives to its dark web data leak portal on

ATF confirms “major incident” after recent Qilin breach claims Read More »

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered government agencies to patch their Citrix NetScaler appliances against an actively exploited vulnerability by Saturday. Tracked as CVE-2026-8452, this high-severity security flaw stems from a memory overflow weakness affecting NetScaler ADC and NetScaler Gateway appliances configured with Gateway VPN or AAA (Authentication, Authorization, and Auditing)

CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday Read More »

Carhartt data breach exposes information of 12.9 million accounts

The ShinyHunters extortion group has published sensitive data from nearly 13 million accounts stolen from clothing retailer giant Carhartt earlier this month, according to data breach notification service Have I Been Pwned. Founded in 1889, Carhartt is an American apparel company with workwear and streetwear manufacturing facilities in Kentucky and Tennessee and more than 3,000

Carhartt data breach exposes information of 12.9 million accounts Read More »

Webinar: How Google Workspace breaches happen and what to do next

Google Workspace has become a critical part of how fast-growing companies operate, giving employees access to email, files, applications, and other business resources. But when attackers find a way into that environment, the same connectivity can create opportunities for a breach to spread. On September 23, 2026, BleepingComputer will host a live webinar titled “Breach

Webinar: How Google Workspace breaches happen and what to do next Read More »

Ubiquiti patches three max severity security vulnerabilities

Ubiquiti has released security patches for three new maximum-severity vulnerabilities that threat actors can exploit remotely without privileges. The first (tracked as CVE-2026-77537) lets unauthenticated attackers compromise unpatched devices by exploiting an improper input validation weakness in the UniFi Protect Application video surveillance management platform. Ubiquiti also addressed a CRLF injection flaw (CVE-2026-77550) that remote

Ubiquiti patches three max severity security vulnerabilities Read More »

Hackers now exploit critical Gitea flaw in code injection attacks

Attackers are actively exploiting a critical-severity vulnerability in the Gitea self-hosted Git service, according to the U.S. Cybersecurity and Infrastructure Security Agency (CISA). Like cloud-hosted GitHub or GitLab SaaS (Software as a Service) platforms, Gitea provides a full suite of DevOps tools, but it is designed to be used as a self-hosted software development platform.

Hackers now exploit critical Gitea flaw in code injection attacks Read More »

Chrome’s ad-blocking champion gets one last update before the curtain falls

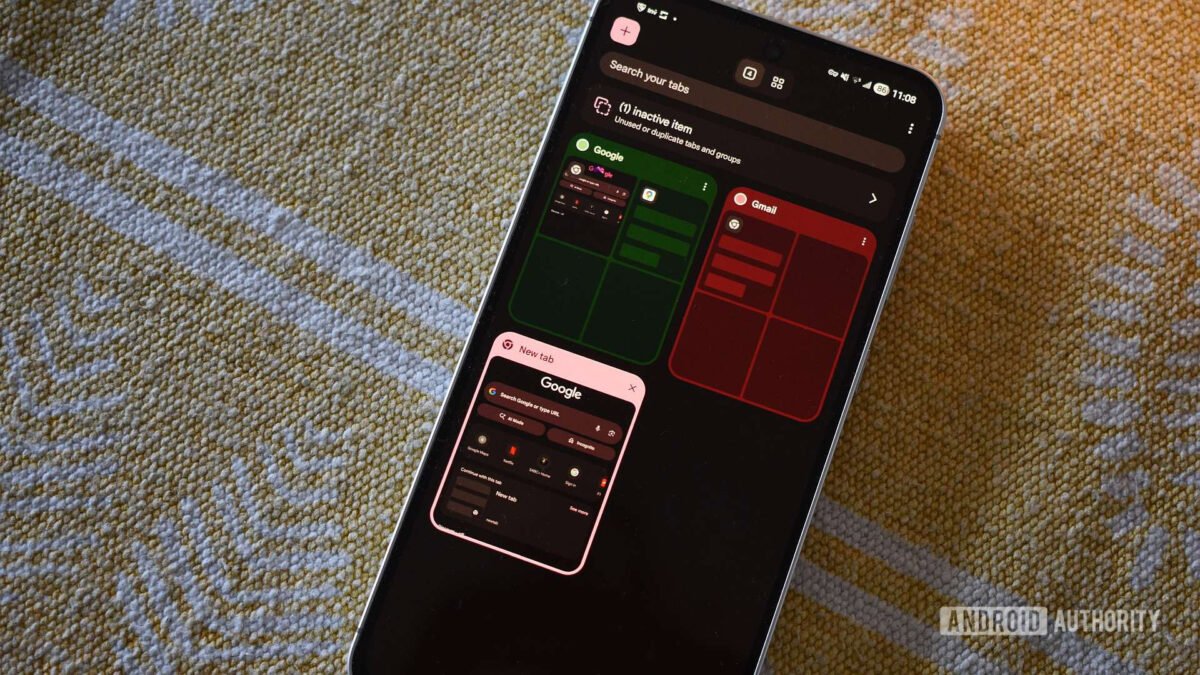
Affiliate links on Android Authority may earn us a commission. Learn more. For many Chrome users, uBlock Origin (uBO) has long been one of those essential browser extensions, quietly sitting in the toolbar and blocking ads without much fuss. But Google’s long-running Manifest V2 crackdown has steadily changed that, and the uBlock Origin team has

Chrome’s ad-blocking champion gets one last update before the curtain falls Read More »

LACMA data breach last year exposed social security and medical data

The Los Angeles County Museum of Art (LACMA) has announced that a breach last year exposed customer and employee information. The museum says that on July 11, 2025, it detected suspicious activity on its systems that had started four days earlier. A month later, the investigation confirmed that the network was compromised. At the time,

LACMA data breach last year exposed social security and medical data Read More »

WhatsApp adds stronger two-step verification, multiple passkeys

WhatsApp has started rolling out several new account security features, including support for multiple passkeys and stronger two-step verification. While the instant messaging service already allowed users to add passkeys for secure logins via fingerprint, Face ID, or screen lock code, it now lets them create separate ones for each platform. “More than a billion

WhatsApp adds stronger two-step verification, multiple passkeys Read More »