Software

Hackers breached over 270 Zimbra servers in ongoing attacks

Threat actors have already compromised over 270 Zimbra instances in remote code execution attacks targeting a high-severity Zimbra Collaboration Suite (ZCS) vulnerability. The ZCS email and collaboration suite is used by hundreds of millions of people and organizations, including thousands of businesses and hundreds of government agencies worldwide. Synacor patched the security flaw (tracked as

Hackers breached over 270 Zimbra servers in ongoing attacks Read More »
Police arrests dozens of suspects in global cybercrime crackdown

Law enforcement agencies from 22 countries helped identify 263 suspects and arrested 58 individuals linked to cybercrime networks coordinated by African crime groups. The “Operation Jackal IV” international joint action targeted West African criminal networks between November 2025 and June 2026. The operation also focused on disrupting the Black Axe cybercrime syndicate, known for its

Police arrests dozens of suspects in global cybercrime crackdown Read More »

South Korean startup platform breach exposes key management failures

In July, South Korea’s government-backed startup support platform, Modu-ui Changup (모두의창업), suffered a data breach. The incident later revealed a critical encryption key management failure, demonstrating how encrypted data can still become exposed when organizations fail to protect encryption keys properly. The platform supports a nationwide startup audition program overseen by South Korea’s Ministry of

South Korean startup platform breach exposes key management failures Read More »

Microsoft Teams now lets admins block external bots from meetings

Microsoft is rolling out a new Teams meeting protection policy that allows administrators to automatically block all identified external bots from joining Teams meetings. This new feature builds on another Teams policy introduced in June that added smarter bot protection, ensuring all detected bots are tagged in the lobby and require organizer approval before joining.

Microsoft Teams now lets admins block external bots from meetings Read More »

ReliaQuest confirms failed data-theft attack after ShinyHunters breach

Cybersecurity company ReliaQuest has confirmed that one of its employees was targeted in a social engineering attack after hackers impersonated a member of the security team. In a statement over the weekend, ReliaQuest said that an attacker called multiple employees and tried to trick them into accessing “a fake ReliaQuest single sign-on (SSO) page behind

ReliaQuest confirms failed data-theft attack after ShinyHunters breach Read More »

Hackers target WordPress sites in miniOrange auth bypass attacks

Hackers are attempting to exploit two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On plugin for WordPress that can be used to forge SAML responses and log in as administrators. The miniOrange SAML SSO plugin turns a WordPress site into a SAML service provider, letting users log in through corporate identity

Hackers target WordPress sites in miniOrange auth bypass attacks Read More »

Unpatched Calix flaw lets hackers bypass NAT to expose internal devices

An unpatched vulnerability in Calix GS7 XGS (GS5239XG) residential routers used by multiple U.S. broadband providers allows remote, unauthenticated attackers to create port-forwarding rules that can expose local network devices to the public internet. The flaw is tracked as CVE-2026-75501 and is described as a missing authentication issue that affects devices running EXOS/6.6.47 firmware. Security

Unpatched Calix flaw lets hackers bypass NAT to expose internal devices Read More »

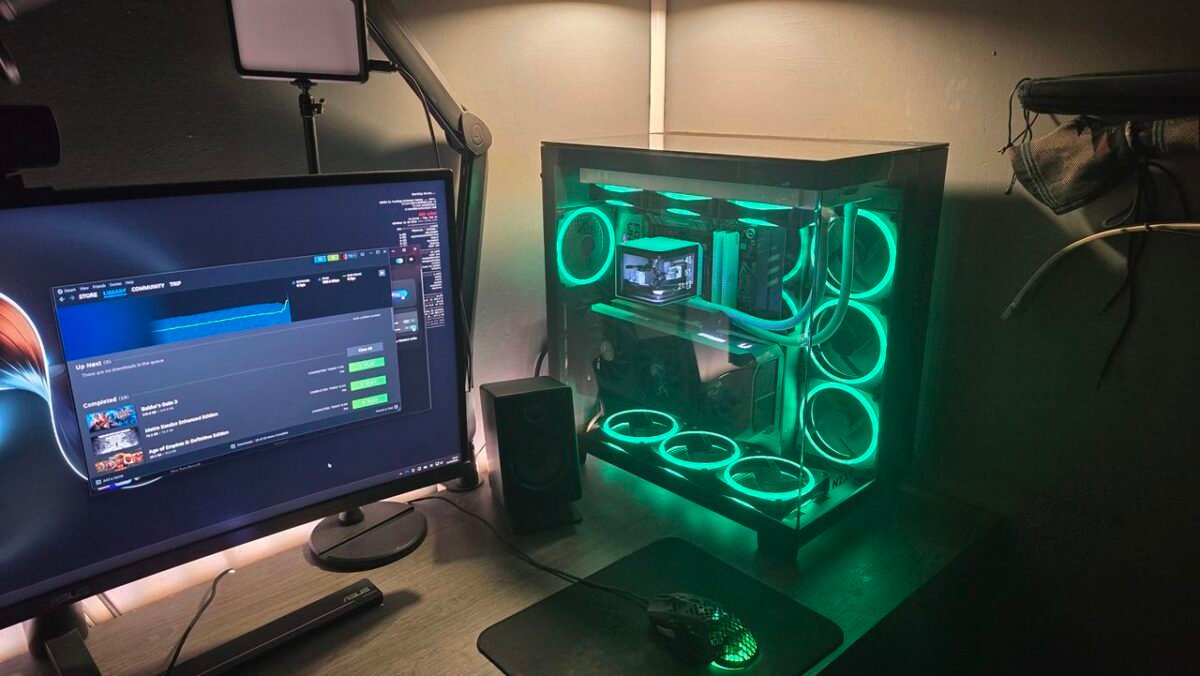
Windows update that breaks some multiplayer games linked to our desire for gaming PCs that light up all the colors of the rainbow

Last week, we covered the very strange occurrence of a bug in the latest Windows update. Yes, a bug in a Windows update, say it isn’t so. Unfortunately, this one does incur our wrath of gamers more than most because it leads to some games becoming unresponsive. Games like Arc Raiders, Marvel Tōkon: Fighting Souls,

Windows update that breaks some multiplayer games linked to our desire for gaming PCs that light up all the colors of the rainbow Read More »

Twitch hit with class-action lawsuit over Amazon AI training: ‘Twitch sent no email, displayed no pop-up notification, and made no announcement’

In yet another unpleasant move in our AI hellscape, Amazon was caught training its generative AI using Twitch stream content earlier this month—a particularly brazen strategy, especially given Twitch’s chief product officer admitted that the data collection was opt-out because “nobody would opt in.” Hmm, I wonder why! Anyway, despite attempts to insist that Twitch

Twitch hit with class-action lawsuit over Amazon AI training: ‘Twitch sent no email, displayed no pop-up notification, and made no announcement’ Read More »

CISA orders urgent patching of actively exploited Zimbra flaw

The Cybersecurity and Infrastructure Security Agency (CISA) has ordered U.S. government agencies to patch an actively exploited vulnerability in Zimbra Collaboration Suite (ZCS) within three days. The Zimbra security team patched the security flaw (tracked as CVE-2026-73570) in version 10.1.20, released on July 20. Successful exploitation allows unauthenticated attackers to gain remote code execution by

CISA orders urgent patching of actively exploited Zimbra flaw Read More »