Software

Nefilim and Hive ransomware affiliate gets 70 months in prison

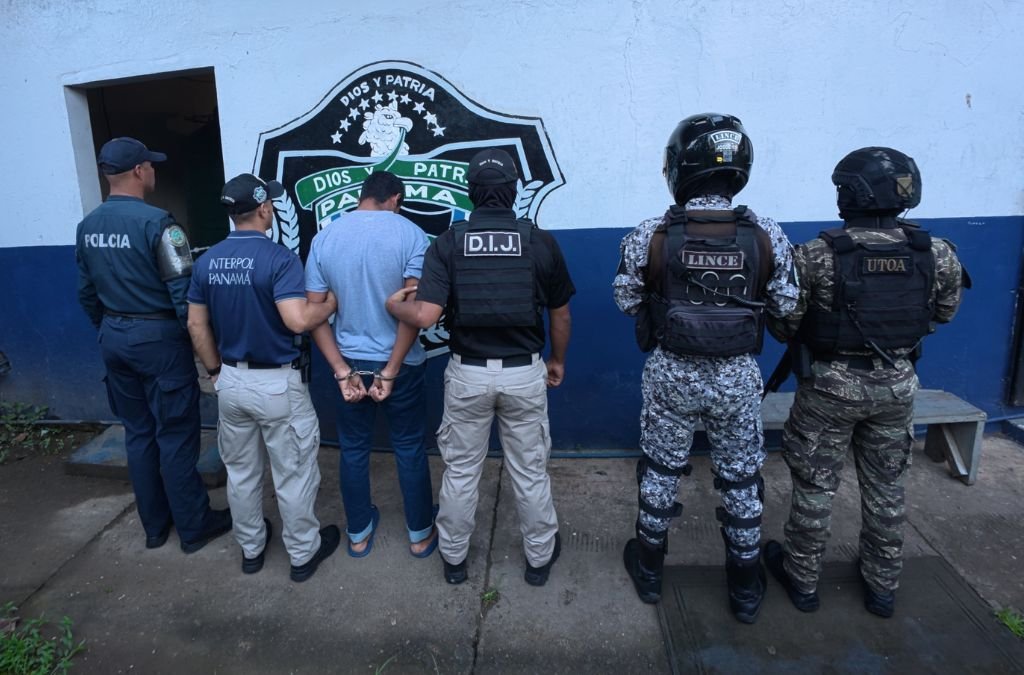
A Ukrainian national was sentenced to 70 months in prison for his role in Nefilim and Hive ransomware attacks targeting hospitals, government entities, and high-revenue businesses worldwide between 2018 and 2021. The sentence follows the extradition of 35-year-old Artem Aleksandrovych Stryzhak to the United States on April 30, 2025, after authorities arrested him in Spain

Nefilim and Hive ransomware affiliate gets 70 months in prison Read More »
CISA warns of hackers now exploiting critical Node2Shell flaw

On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed that hackers have begun exploiting a critical Brotli vulnerability known as Node2Shell, Broccoli2Shell, and HTTP2Shell. Tracked as CVE-2026-111497, this critical-severity flaw stems from an out-of-bounds write weakness in the Brotli decoder used to expand data compressed with Google’s widely popular Brotli lossless compression algorithm.

CISA warns of hackers now exploiting critical Node2Shell flaw Read More »

Hackers now scanning systems for recently-patched Oracle flaw

Attackers have begun probing the Internet for systems unpatched against a recently disclosed critical Oracle E-Business Suite (EBS) vulnerability. Discovered in a core component of EBS’s Application Object Library and tracked as CVE-2026-101767, this flaw lets unauthenticated threat actors with HTTP network access take over vulnerable systems in low-complexity attacks. Oracle released security updates to

Hackers now scanning systems for recently-patched Oracle flaw Read More »

Police arrests 95 suspects in international CSAM crackdown action

Law enforcement authorities from 17 countries in Latin America and Europe have arrested 95 suspects in an INTERPOL-coordinated operation targeting the distribution of child sexual abuse material (CSAM) through online messaging groups. The joint action, dubbed International Effort Confluencia, included four law enforcement operations between March 2026 and September 2026. “Effective cross-border cooperation between law

Police arrests 95 suspects in international CSAM crackdown action Read More »

Citizen Lab says governments are abusing online ads to hack people with ‘zero-click’ spyware

Security researchers at digital rights unit Citizen Lab say government spyware makers are abusing global advertising networks to target and hack devices by serving malicious online adverts. A new report published Thursday by the University of Toronto lab, which investigates surveillance and digital rights abuses, said an Israeli company called Discover-Tech allows spyware makers to

Citizen Lab says governments are abusing online ads to hack people with ‘zero-click’ spyware Read More »

UK Legal Aid Agency: Hackers stole records dating back to 1978

The Legal Aid Agency (LAA), an executive agency of the UK’s Ministry of Justice that manages the country’s Public Defender Service, says attackers who breached its IT systems in April 2025 stole records dating back to 1978. The agency employs around 1,250 staff, oversees billions in legal funding, and works with approximately 2,000 providers, including

UK Legal Aid Agency: Hackers stole records dating back to 1978 Read More »

The Blind Spots of Agentic Pentesting and How to Close Them

By Sila Ozeren Hacioglu, Security Research Engineer at Picus Security. For years, security teams had a window of several weeks between a CVE going public and attackers exploiting it. Every year, that window got smaller. Then Mythos-class models arrived, and attackers can now weaponize a new CVE within hours. That leaves security teams very little

The Blind Spots of Agentic Pentesting and How to Close Them Read More »

Cisco patches new Secure Email Gateway zero-day exploited in attacks

Cisco has patched another actively exploited zero-day flaw in its Secure Email Gateway (SEG) that lets remote unauthenticated attackers execute commands with root privileges. Tracked as CVE-2026-76519, this vulnerability stems from a relative path traversal weakness in SEG’s Advanced Malware Protection (AMP) feature, caused by improper handling of email attachments. Threat actors can exploit this

Cisco patches new Secure Email Gateway zero-day exploited in attacks Read More »

Ledger asks sellers across Asia to halt sales after supply-chain attack

Ledger is asking resellers and distributors in Southeast Asia and Hong Kong to halt wallet sales and remove products from shelves while it investigates hardware implant incidents. The company announced the decision in response to discovering that devices purchased from CryptoBilis had been modified to steal seed phrases used to access crypto assets and send

Ledger asks sellers across Asia to halt sales after supply-chain attack Read More »

FBI raids DPRK IT worker laptop farms in Texas, US nationals arrested

The U.S. Department of Justice (DoJ) has disrupted the Famous Chollima threat group’s operations by arresting two suspects, charging 14 individuals, and seizing nearly 187 laptops used in North Korean remote IT worker schemes. Famous Chollima (a.k.a. WageMole) is commonly tracked as a North Korean threat actor associated with fraudulent IT-worker schemes that generate revenue

FBI raids DPRK IT worker laptop farms in Texas, US nationals arrested Read More »