Software

Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks

Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited in attacks targeting firewalls. The vulnerability affects the PAN-OS management interface and lets authenticated attackers with network access execute code as root on vulnerable devices. Palo Alto Networks confirmed in a security advisory published Wednesday

Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks Read More »
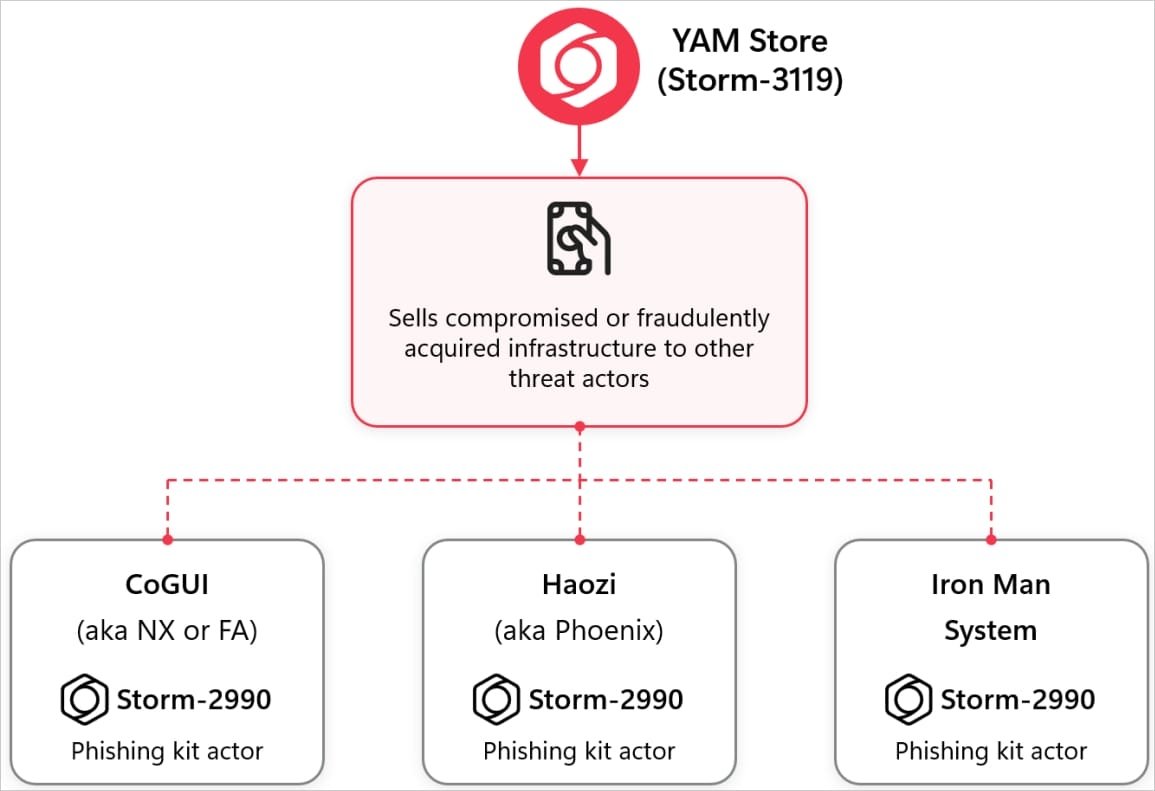
Global takedown hits network behind 1 billion phishing messages

A massive cybercriminal ecosystem facilitating more than a billion malicious messages targeting over 75,000 organizations across 150 countries has been disrupted by law enforcement agencies and partners worldwide. Since the start of the year, more than 750 million malicious messages have been aimed at Microsoft customers via email and SMS texts. Following an investigation initiated

Global takedown hits network behind 1 billion phishing messages Read More »

CISA warns admins to immediately fix Ivanti flaw exploited as zero-day

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) urged security teams to immediately patch an Ivanti Connect Secure (ICS) flaw exploited in zero-day attacks since at least October 1st. Tracked as CVE-2026-104935, this high-severity authentication bypass vulnerability lets remote threat actors without privileges execute arbitrary commands on targeted ICS systems in low-complexity attacks that don’t

CISA warns admins to immediately fix Ivanti flaw exploited as zero-day Read More »

OpenAI employee arrested for allegedly using AI and toilet paper to record confidential meetings – FBI director Kash Patel jumps at the chance to say AI companies are ‘essential’ for national security

An OpenAI engineer has been arrested and charged for using (or endeavoring to use) an audio recording device to spy on confidential company communications. That’s according to the US Department of Justice, and while commercial espionage is nothing new, there’s a certain sardonic twist to this one: it seems the accused employee did so with

OpenAI employee arrested for allegedly using AI and toilet paper to record confidential meetings – FBI director Kash Patel jumps at the chance to say AI companies are ‘essential’ for national security Read More »

Hirudo Android malware replaces banking apps to evade security checks

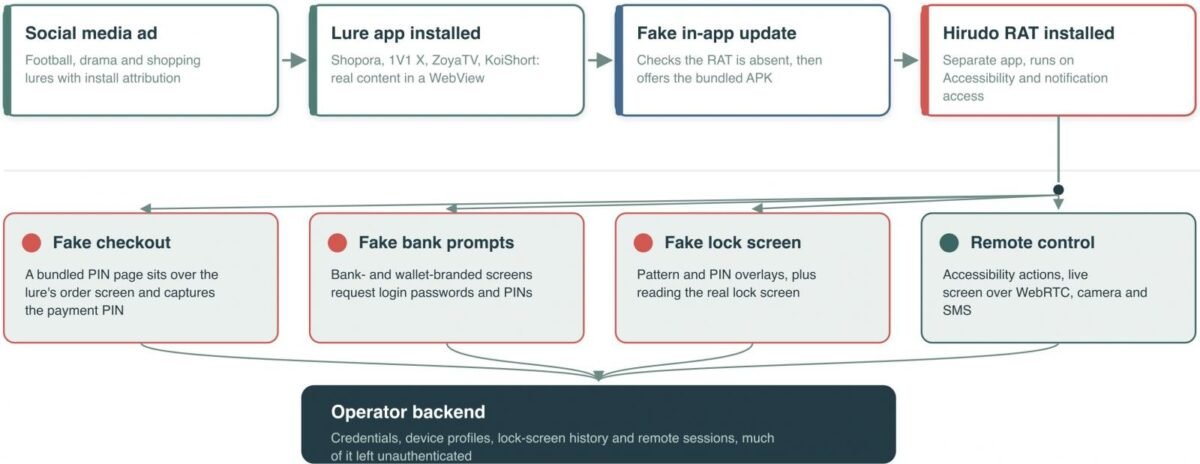
A new Android malware called Hirudo steals bank account credentials by replacing legitimate banking apps with modified versions that disable security checks. Researchers identified malicious copies of eight banking apps that use a hooking engine to bypass app-signature, Accessibility, and Play Integrity checks by substituting certificate information or returning empty lists. Threat actors can use

Hirudo Android malware replaces banking apps to evade security checks Read More »

‘123456’ password was all a hacker reportedly needed to expose over 8 million people’s personal data

Please, please, please do not use ‘123456’ as any kind of password. I know that may seem obvious, but apparently it bears repeating if a recent hack of Denmark’s Central Register of Persons (CPR) is anything to go by. To recap, the CPR administration said earlier this month that it had become aware of a

‘123456’ password was all a hacker reportedly needed to expose over 8 million people’s personal data Read More »

Microsoft: Recent Windows updates may trigger Remote Desktop failures

Microsoft has confirmed that non-admin users may be unable to connect to devices via Remote Desktop after installing recent Windows updates if the “Administrator protection” security feature is enabled. This feature began rolling out with the KB5067036 preview cumulative update to systems running Windows 11 24H2/25H2 in October 2025, and it is now enabled by

Microsoft: Recent Windows updates may trigger Remote Desktop failures Read More »

Steam’s new Big Art Mode is a lovely visual upgrade for my living room setup

Steam’s Big Picture Mode just got a big visual overhaul that puts game art in the spotlight, and my living room setup has never looked better. The new mode is rolling out of beta with the latest Steam client release. If you’re all up-to-date, you can enable it within Big Picture Mode. Just head to

Steam’s new Big Art Mode is a lovely visual upgrade for my living room setup Read More »

Docker Hub flaw let attackers impersonate users, tamper with images

Docker has disclosed a critical vulnerability (CVE-2026-105445) in Docker Hub that let attackers access another user’s container repositories using a personal access token (PAT). Docker Hub is an online registry for storing, sharing, and downloading container images – templates that package everything needed for an application to run in an isolated environment. In Docker Hub,

Docker Hub flaw let attackers impersonate users, tamper with images Read More »