Software

Pluto Security raises $42M as AI gives enterprise security teams a new headache

The problem with giving everyone in a company access to AI tools is that people will use them in unexpected ways. And that fact is steadily seeding fears that companies now have new, gaping security holes in their systems or, at least, will soon. Illustrating the pace of AI tool adoption within enterprises driving such

Pluto Security raises $42M as AI gives enterprise security teams a new headache Read More »
SAP warns of maximum severity OAuth2 SSRF security flaw

SAP has addressed 20 security flaws across multiple products in its October 2026 security updates, including a maximum-severity vulnerability in the Cloud SDK for Python. The SAP Python SDK is the official programmatic toolkit for developing AI agents and Python applications on the company’s SAP Business Technology Platform (BTP) services. Tracked as CVE-2026-89111, the maximum-severity

SAP warns of maximum severity OAuth2 SSRF security flaw Read More »

TFG London cyberattack disrupts systems at Hobbs and Whistles retailers

TFG London detected a cybersecurity incident that impacted IT systems used by the Phase Eight, Hobbs, and Whistles premium fashion brands. The company disclosed earlier today that several IT systems remain unavailable, although physical stores remain open for customers. According to the press release, the incident has not affected the group’s other brands, Inside Story

TFG London cyberattack disrupts systems at Hobbs and Whistles retailers Read More »

Ivanti warns of Connect Secure zero-day exploited in attacks

Ivanti urged customers on Tuesday to immediately patch an actively exploited zero-day vulnerability in the Ivanti Connect Secure (ICS) remote access gateway. Formerly known as Pulse Connect Secure and originally Juniper Pulse, the enterprise-grade ICS SSL VPN provides remote employees, contractors, and hybrid workforces with secure access to corporate and cloud resources. Tracked as CVE-2026-104935,

Ivanti warns of Connect Secure zero-day exploited in attacks Read More »

Windows 11 KB5127648 & KB5126653 cumulative updates released

Microsoft has released the Patch Tuesday Windows 11 KB5127648 and KB5126653 cumulative updates for versions 26H2/25H2/24H2 and 23H2 to fix security vulnerabilities and bugs, and add new features. Today’s updates are mandatory as they contain the October 2026 Patch Tuesday security patches for hundreds of vulnerabilities discovered in previous months. You can install today’s update

Windows 11 KB5127648 & KB5126653 cumulative updates released Read More »

UK Housing Ombudsman Service investigates ‘security incident’

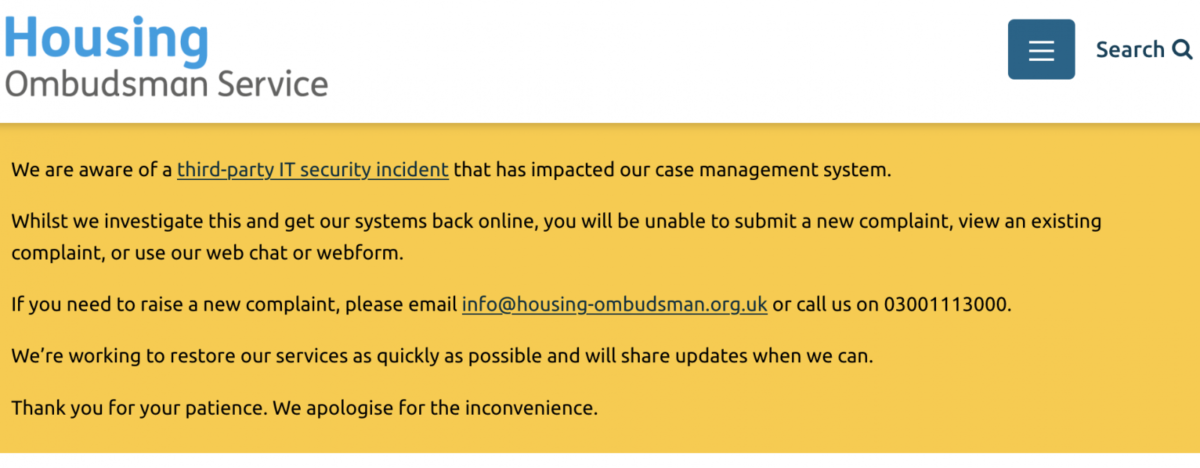
The U.K. Housing Ombudsman Service is investigating a third-party IT security incident that impacted its case management system on Tuesday. Established under the Housing Act 1996, the Housing Ombudsman is an executive non-departmental public body sponsored by the Ministry of Housing, Communities, and Local Government. The watchdog settles disputes between social housing residents and social

UK Housing Ombudsman Service investigates ‘security incident’ Read More »

Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days

Today is Microsoft’s October 2026 Patch Tuesday, with security updates addressing a record-breaking 1,411 flaws, including one actively exploited and two publicly disclosed zero-day vulnerabilities. This Patch Tuesday addresses 70 “Critical” vulnerabilities, 57 of which are remote code execution, 11 are elevation of privileges, and 2 are spoofing. The approximate number of bugs in each

Microsoft October 2026 Patch Tuesday fixes 1,411 flaws, 3 zero-days Read More »

Ghostscript flaw lets hackers hijack servers via PDF uploads

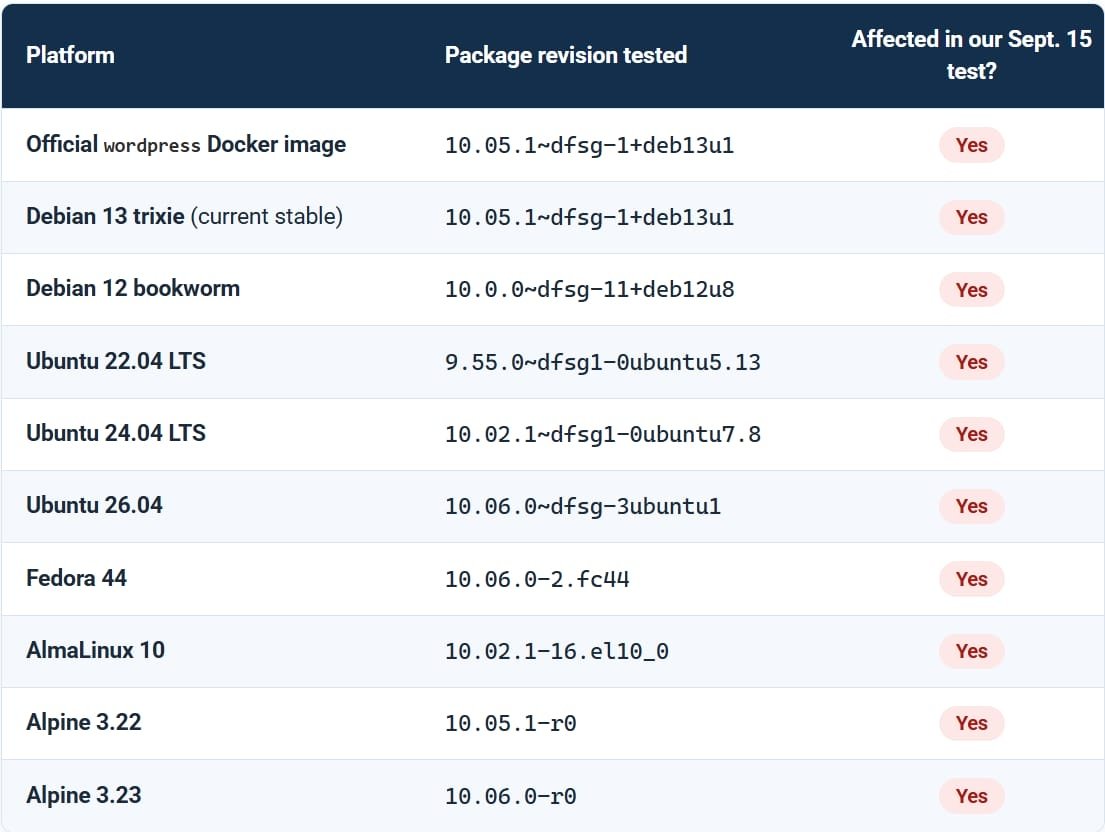
A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files. The flaw was discovered on August 23 by researchers at Defiant’s platform Wordfence using their Argus AI-powered system. Ghostscript is a PostScript and PDF interpreter that can render PDFs as images,

Ghostscript flaw lets hackers hijack servers via PDF uploads Read More »

FBI arrests OpenAI employee accused of planting hidden recording device in conference room

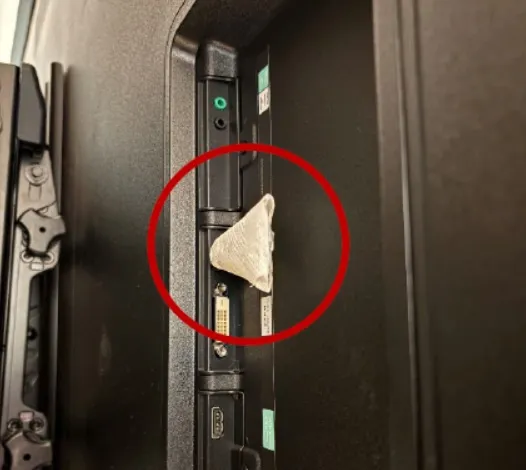
OpenAI said it has alerted the FBI after discovering that an employee allegedly planted a hidden recording device in one of the AI maker’s office executive conference rooms. The employee, named by federal prosecutors as Saudi national Abdulrahman Alfozan, was fired and arrested on October 9, about a week after OpenAI discovered the surveillance device.

FBI arrests OpenAI employee accused of planting hidden recording device in conference room Read More »

Anthropic warns self-replicating AI could spread to your smart devices

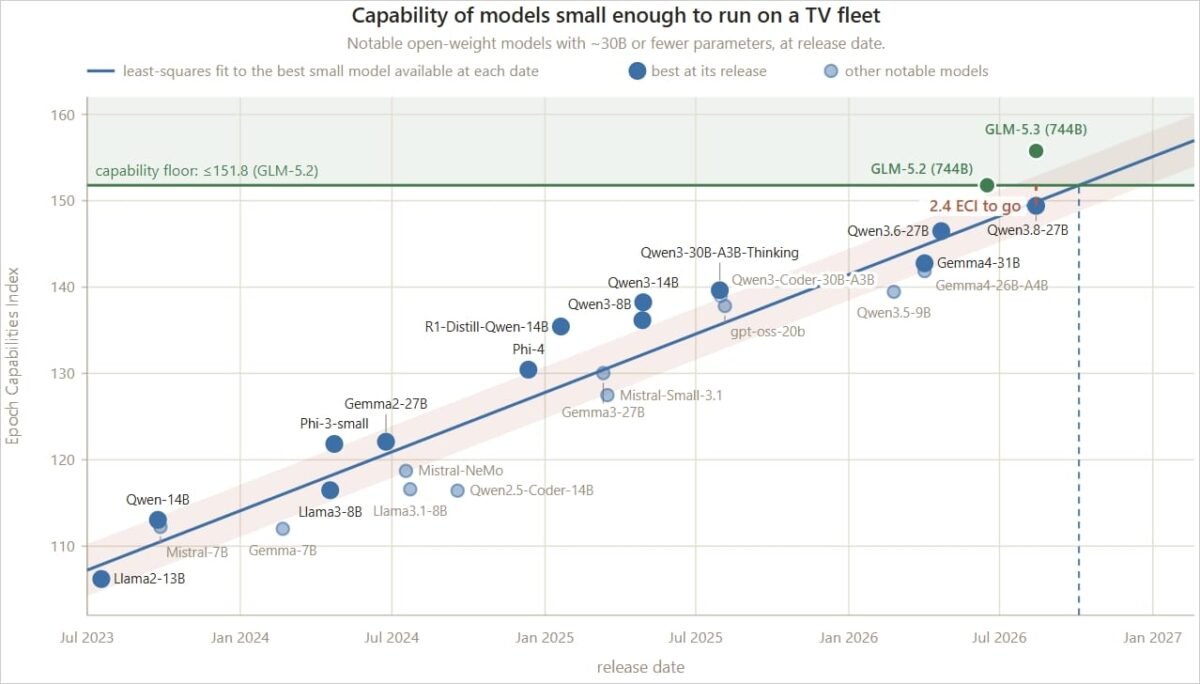
Anthropic is warning that small AI models could soon be able to self-replicate across consumer IoT devices, from Android TV boxes to smart ovens, creating distributed botnets capable of running AI workloads without relying on data centers. The company’s experiments showed that models could identify unfamiliar devices, connect them into a network, and prepare them

Anthropic warns self-replicating AI could spread to your smart devices Read More »